Posted on

iOS 26.1 Beta 2 Arrives With Additional Apple Intelligence Languages

José Adorno/BGR

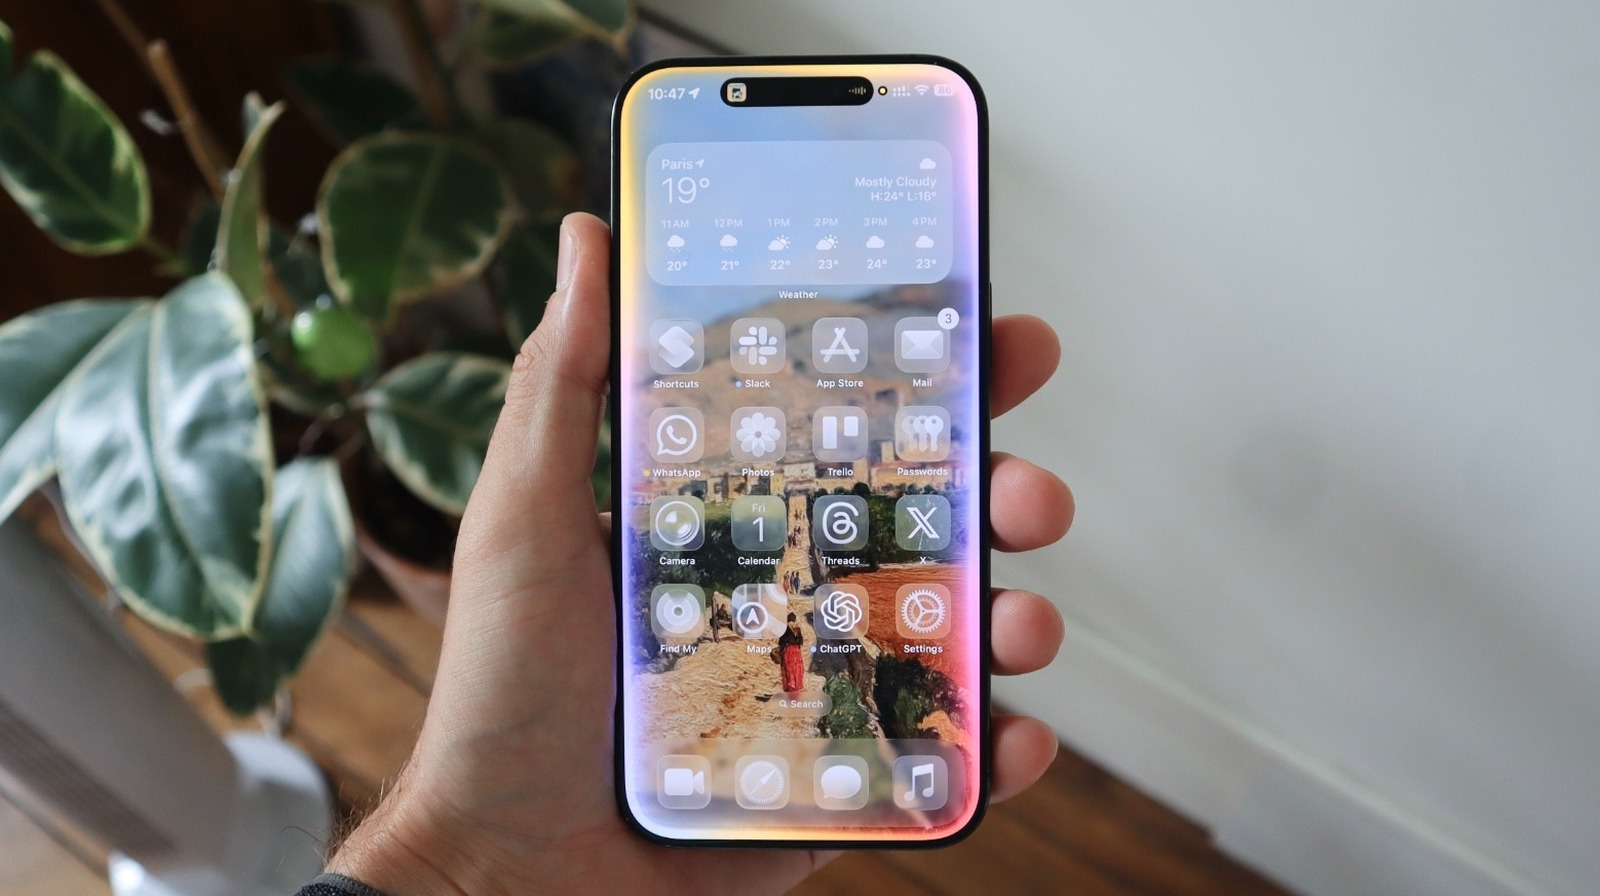
Following the release of the first iOS 26.1 beta, Apple has now rolled out its second test version. While we’re still checking to see what the new build has to offer, the company is likely focused on refining features that were introduced previously.

One of the most notable additions in iOS 26.1 beta is the expansion of Apple Intelligence to more languages. Apple’s AI now supports Danish, Dutch, Norwegian, Swedish, Turkish, Vietnamese, Chinese (Traditional), and Portuguese (Portugal).

Apple is also improving Live Translation language support, adding Chinese (Simplified and Traditional), Italian, Japanese, and Korean. With the previous beta version, the company added a new gesture to the Apple Music app, a Liquid Glass design touch to the keypad on the Phone app, and improved the list view on the Calendar app. More importantly, Apple continues to work on fixing bugs that have been plaguing iOS 26, including an issue with the iPhone 17 camera, unreliable Wi-Fi experiences, and more.

iOS 26.1 beta paves the way for two important iPhone features

José Adorno/BGR

With the first beta of iOS 26.1, Apple began working to add support for the Model Context Protocol, which could let third-party LLMs, such as ChatGPT or Gemini, read data from various apps and perform actions on behalf of users. While it’s not available to test, this feature means that the iPhone will soon enter the agentic AI world, where you could ask ChatGPT to write you a message on WhatsApp or edit a photo in a specific way (all of the things Apple wants to do with its smarter, more conversational Siri).

Besides that, beta references in iOS 26.1 suggests Apple is readying support for third-party smartwatches. It’s unclear if the company will restrict this functionality to the European market or if it could expand globally. After all, Apple needs to add third-party smartwatch support by June 2026 to satisfy European Commission rules.

Alongside iOS 26.1 beta 2, Apple seeded the second test versions of iPadOS 26.1, macOS Tahoe 26.1, watchOS 26.1, tvOS 26.1, and visionOS 26.1. We’ll let you know if we find anything new while exploring the latest betas.

Source

Posted on

IT Sustainability Think Tank: Distinguishing the green washers from the

Calculating carbon emissions is not as simple as it seems. When greenwashing meets poor carbon accounting, progress in establishing industry standards is delayed. This can erode trust in businesses, stalling sales and inhibiting economic growth.

At Digital Catapult we work across high-value sectors to accelerate the practical application of deep tech innovation and equip the UK to be future-ready.  

We do this by driving industrial decarbonisation, and recognise that a cross-sector framework is needed to achieve greater transparency, accountability, and cross-sector collaboration.

This is where innovation can provide an answer, enabling businesses to distinguish the green washers from the green winners, decarbonising operations safely and sustainably, while driving industrial supply chain resilience too. 

A cross-sector decarbonisation framework 

With global energy demand projected to rival Japan’s total consumption by 2030, power is part of a bigger story. Datacentres drive water consumption, land competition, electronic waste, and noise pollution. Without a standard framework, innovators often struggle to identify what a solution might look like, driving some to fall victim to unreliable partners, as they commence their journey towards net-zero.  

The UK policy to reach net-zero carbon emissions by 2050 has accelerated innovation in the commercial space, prompting technology providers to explore new solutions at an unprecedented speed.

The risk here, however, is that many businesses misunderstand carbon accounting or the environmental impact of their operations, prompting some to look for a quick-fix or a partnership with a company guilty of greenwashing.  

In the UK, large companies must disclose Scope 1 and 2, but Scope 3 reporting is largely voluntary. This loophole matters. Much of the tech sector’s footprint lies in Scope 3, which come from outsourced datacentres, cloud services, and supply chains.

For companies reliant on global datacentres and sprawling supply chains, this creates a convenient blind spot, and risks companies falling short of their decarbonisation targets and stalling the environmental progress of entire sectors and markets. 

As such, an intervention is key to mitigate greenwashing in supply chains, and bolster supply chain resilience, which can be achieved when deep tech innovation is practically applied to industry, like we’ve achieved with some of our interventions.   

Using deep tech to solve its own sustainability challenges 

At Digital Catapult we recognise that while deep tech innovation often depends on energy-intensive infrastructure that can create new pressures elsewhere, we need a framework grounded in systems thinking.

This should be adaptive, holistic, and connected, and is why we are working on a framework that is flexible to change, can account for a range of impacts, and will recognise unintended consequences. This will ultimately empower businesses to apply better deep tech solutions to their operations, equipping them with the tools necessary to be future-ready. 

The resulting offerings may include artificial intelligence (AI) that can optimise industrial processes, reduce waste, and increase efficiency or quantum computing, which may one day process vast datasets at a fraction of today’s energy. Meanwhile, the Internet of Things is already making supply chains more transparent and energy efficient.

At Digital Catapult, we enable deep tech startups to scale successfully, and we have first-hand knowledge of how deep tech innovation could be used to drive industrial decarbonisation and mitigate greenwashing, particularly when it’s used within a valid framework.   

Meeting the demand for decarbonisation  

Digital Catapult’s AI innovation programme, which considers how AI can be used for decarbonisation, is developing a framework that could be used across industries and will solve some of the challenges that come with carbon accounting and deep tech’s environmental impact.

It will also enable businesses across sectors to identify where deep tech innovation like AI can deliver the greatest decarbonisation benefits, understand potential trade-offs, and make more informed decisions about deep tech adoption that mitigates the risk of green washing.  

Similarly, our supply chain work focuses on strengthening industrial resilience in the UK while creating greater transparency around Scope 3 emissions, which remain a critical blind spot in carbon accounting.

Through the Logistics Living Lab, we are applying deep tech innovations such as AI and distributed ledger technology to reduce inefficiencies like empty lorry journeys.

By cutting unnecessary miles on the road, this approach not only lowers emissions across logistics and haulage but also demonstrates how targeted deep tech solutions, when embedded within a wider framework, can deliver measurable decarbonisation while reducing the risks of greenwashing, as well as making supply chains more resilient.   

If the UK is to reach its net-zero targets, it must look beyond surface-level commitments and tackle the structural challenges that allow greenwashing to persist.

Deep tech alone will not deliver sustainable change, but when embedded in robust, cross-sector frameworks it can provide the transparency, accountability, and adaptability businesses need.  

By applying systems thinking, addressing Scope 3 blind spots, and deploying innovation responsibly, we can ensure deep tech becomes a force for genuine decarbonisation, and that industrial supply chain resilience can be achieved across industries. 

The winners will be those who embrace this approach, building trust, resilience, and a greener industrial future.

Source

Posted on

Cohesity CEO: ‘The Middle East is moving faster than any

Cohesity has become a prominent name in cyber resilience, as enterprises worldwide look for smarter ways to secure and recover data in an age of increasingly sophisticated threats. For CEO Sanjay Poonen, the company’s mission reflects this shift in urgency: “Our mission is to protect, secure and provide insights into the world’s data. The largest organisations in the world, the biggest brands, rely on us for cyber resilience.”

Traditional backup approaches are no longer enough as ransomware evolves. Poonen highlights how enterprises today face persistent threats from nation-state actors across the US, Europe and the Middle East. To address this, Cohesity has built what it describes as an immutable, zero-trust security platform designed for fast recovery.

The Middle East, he says, is particularly important in this landscape. Countries across the region are investing heavily in digital transformation and AI, creating opportunities and challenges for data protection.

Cohesity has established a strong presence in the region, working with banks, hospitals, telcos, and public sector institutions. “The Middle East is moving faster than any other region when it comes to data resilience,” Poonen says. “We have hundreds of customers here and are working closely with partners to deploy AI-powered solutions tailored to the market.”

A key element of Cohesity’s approach is the integration of AI into its platform. Its product, Gaia, leverages generative AI to provide advanced data insights, anomaly detection, and threat scanning, allowing organisations to protect and make sense of their data in ways that traditional backup solutions cannot.

“We’ve modernised the discussion from traditional storage to security. Generative AI on top of data is the next frontier for enterprises everywhere, including the UAE and wider Middle East,” says Poonen.

Looking ahead, Cohesity’s global priorities revolve around three strategic areas – multi-cloud data protection, advanced security capabilities, and AI-driven intelligence on the data being protected. “These three pillars are central to our innovation strategy, not just in the US but globally, and the Middle East is no exception,” he adds.

Poonen also emphasises the role of events like Gitex, where he met with Computer Weekly, in fostering awareness and collaboration. “This conference is incredible, it brings together 200,000 people and showcases how technology can enable resilience everywhere,” he said.

With cyber threats evolving rapidly and data becoming a critical economic asset, Cohesity sees its role as helping organisations navigate the complex intersection of AI, cloud adoption, and cyber resilience. For the Middle East, a region accelerating in AI adoption and digital transformation, the company’s CEO believes there is a unique opportunity to establish robust, secure, and future-ready data infrastructure.

Source

Posted on

Why Keir Starmer’s mandatory national digital ID system may be

With nearly three million people – so far – signing an online petition against the introduction of “digital ID cards”, the government is already fighting to reclaim the initiative after prime minister Keir Starmer’s botched announcement of plans for a mandatory national digital identity scheme.

Civil service officials last week attempted to quell the second uproar of the year from private sector digital ID app providers in a behind-closed-doors meeting, while this week (Monday 13 October) new technology secretary Liz Kendall attempted to face down MPs from all parties in a House of Commons debate as they expressed their concerns and protestations at the plans.

Kendall was correct when she told MPs: “There is a lot of misinformation out there about this proposal.” But she did not acknowledge that any misinformation was largely a result of the government’s poor communication around the original announcement.

As fintech industry body Innovate Finance – a supporter of digital identity – put it: “The reaction, frankly, has been to focus on the worst-case scenario – ‘compulsory digital ID’ is being framed as an erosion of civil liberties, a gateway to mass surveillance, and a tool of digital exclusion. It’s all fear and no finesse.”

Christopher Holmes, a Conservative peer who has long been an advocate for digital identity, said: “The government’s current approach, suggesting mandatory digital ID to stop illegal immigration, is going about it in precisely the wrong way.” 

Based on discussions with industry insiders, however, it may in fact be the case that Starmer’s mandatory national digital ID scheme will prove to be neither mandatory nor national.

What, exactly, will be mandatory?

Starmer’s announcement seemed clear: it will be mandatory for anyone seeking a job in the UK to prove their right to work using a government digital identity app on their smartphone – with limited exemptions for those unable to do so.

However, the language used in the Commons by Kendall was subtly different. She talked about “making ID checks both mandatory and digital for all employers”. Her speech tried to focus on the wider benefits of digital identity, citing the need to modernise public services and make them easier to access in a digital age.

Years from now, having your ID on your phone will feel like second nature, putting more power directly into people’s hands and giving them more control over how they interact with government services. That is worth striving for Liz Kendall, technology secretary

“Years from now, when we look back, I believe that having your ID on your phone will feel like second nature, putting more power directly into people’s hands and giving them more control over how they interact with government and the whole range of services. That is something worth striving for,” she said.

As shadow technology secretary Julia Lopez pointed out, the previous Conservative government had already introduced mandatory right-to-work checks for employers and launched a mechanism whereby a digital identity app can be used, voluntarily, to prove an individual’s right to work in the UK. Most UK citizens will have had to prove their right to work (RTW) using physical documents such as a passport.

Any apps used as part of RTW checks have to be approved through the government-backed Digital Identity and Attributes Trust Framework (DIATF), which was given a statutory basis through the Data (Use & Access) Act (DUA), which received Royal Assent in June.

Run by the Office for Digital Identities and Attributes (OfDIA), nearly 50 third-party identity service providers (IDSPs) have received approval under DIATF for their apps to be used for RTW and other statutory government checks, such as age verification or registering as a company director.

Kendall confirmed to MPs that the government will bring legislation during this Parliament – so, before 2029 – for “making ID checks mandatory and digital”. She said there will not be a central database of digital identities, and there will be no sanction or penalty for people if they do not have a digital ID – only for employers that do not conduct RTW checks.

The only legal change the government has proposed so far is that RTW checks will have to be conducted digitally. There will be a government digital identity app that people can use to digitally prove their right to work, but the question remains: will they be compelled to use the government app, or will any app from a DIATF-approved IDSP be acceptable?

What are officials saying in private?

Last week, officials from the Department for Science, Innovation and Technology (DSIT) and OfDIA met with industry representatives in a second attempt this year to quell fears that the government is looking to squeeze private sector suppliers out of the digital identity market – despite years of investment in building third-party apps.

The first attempt came after the announcement of the Gov.uk Wallet and its proposed use for age verification – for example, when buying alcohol or accessing age-restricted online services. Many IDSPs specialise in age verification and have spent millions of pounds developing, testing and proving their capability to determine someone’s age using facial verification through a smartphone app.

Then technology secretary Peter Kyle was forced to meet with suppliers in May to assure them the government had no intention of muscling in – only that the government wants to play a role and it would be strange not to offer its own app. Kyle’s reassurances were warmly received, and supplier executives left the meeting confident that government and industry would be working hand-in-hand going forward.

So, when Starmer announced that the government would be further treading on the IDSPs’ turf, there was understandable outrage.

At the meeting last week, civil service officials outlined how Starmer’s plans would be brought to fruition.

IDSPs were told that OfDIA chief executive Hannah Rutter would be moving into a new role, leading development of the policy and overseeing a consultation planned for early 2026. They heard that Rutter would be replaced at OfDIA by John Peart, who is seen by suppliers as supportive of the private sector’s role. When asked by Computer Weekly, DSIT would not confirm or deny the appointments.

The consultation process – calling for, and responding to, submissions – is likely to take about a year. Draft legislation would then be put before Parliament in 2027, with the new government digital ID scheme likely to be in place by mid-2028, about a year before the next general election.

The legislative process will not be easy. As David Crack, chair of industry body the Association of Digital Verification Professionals, told Computer Weekly, many Labour MPs are opposed to the concept of mandatory digital identity, opposition parties are lining up against it, and because the policy was not included in Labour’s manifesto, the House of Lords may find it constitutionally acceptable to delay or even deny its approval. If millions of voters are against the proposals too, it’s not a policy likely to be enacted in a general election year.

“There is a plan – for a plan for a national ID scheme – but not an [actual] plan. Realpolitik will prevail,” said Crack.

During the meeting with IDSPs, DSIT officials reiterated that measures introduced by the DUA Act will still be implemented.

Significantly, this includes the launch of an “information gateway” which will allow IDSPs to access government-held data as part of the process of confirming people’s identities digitally – for example, passport or driving licence checks – greatly expanding the range of public data that non-government apps can use as credentials to prove that app users are who they say they are.

Well before the likely launch of a government digital ID scheme in 2028, therefore, there will already be a wide variety of digital identity apps and services on the market and already in use by people choosing voluntarily to prove their right to work digitally.

If use of those apps numbers in the millions by 2028, will legislation really force them to move to a government-developed app instead?

Crack said DSIT officials told suppliers they are open to ideas on how to implement mandatory digital RTW checks. “Note, mandatory RTW checks, but not necessarily a mandatory digital ID scheme,” he said. Crack believes that “government is listening”.

Others in the industry are less convinced. “The truth is out – a confirmation that the government made a policy decision to go ahead and do this stuff themselves. We are told the DUA Act will be continued, but my sense is that they see the private sector as interim or peripheral,” said one supplier executive, who asked to remain anonymous.

However, stakeholders across the digital identity sector agree on two things.

First, that Starmer’s announcement has propelled digital identity into a topic for national debate – something even the most worried suppliers have welcomed.

And second, that the manner of Starmer’s announcement – linking digital ID to tackling illegal immigration – means the public will need to be educated on what digital identity really means.

Dispelling the myths

With nearly three million signatories, the petition against the government proposal is one of the largest such online protests, but the statement people sign up to support says, “We demand that the UK government immediately commits to not introducing a digital ID card”.

The government has failed to establish to the public that digital identity is not an attempt at “ID cards by stealth” – and the highly publicised support for the policy from the Tony Blair Institute has not helped to dispel such concerns, given Blair was the prime minister who tried to introduce physical ID cards during the 2000s.

Furthermore, critics have lined up to attack the use of a centralised government database – but Kendall confirmed there is no such plan, there never was, and as anybody familiar with how digital identity works would explain, the technology relies on the secure sharing of credentials, not large amounts of personal data or referencing an identity database.

For example, an age verification app simply confirms that the holder is over 18 when buying alcohol. It shares a digital credential saying “yes” when asked, “Is this person over 18?” – the app does not need to identify the person to the retailer in any way.

Lurid newspaper headlines have warned of US tech companies getting their hands on UK citizens’ personal data, with particular fears over the involvement of Palantir, the controversial data integration supplier that works closely with US military and intelligence services, as well as the NHS. One MP in the Commons debate warned of “writing Fujitsu a blank cheque” – a reference to the shamed IT services supplier that developed the Horizon system at the heart of the Post Office scandal.

However, Kendall confirmed that the government app will be developed in-house, by the Government Digital Service – there are no plans to award a contract to a single supplier to develop the digital ID software from scratch.

The software will be a continuation of existing developments – notably, Gov.uk One Login, the digital identity system that will become the standard way to log in to online public services and is already in use by many government websites.

It’s likely that the digital ID system will use the Gov.uk Wallet to store digital credentials, provided by the government, that prove the holder is who they say they are and that they have the right to work in the UK – much the same as the existing private sector apps that are used for the same purpose today.

By the time any legislation is passed, the amount of further development needed for One Login and the digital wallet is likely to be comparatively minimal – and certainly not require a huge new software development project.

Those plans are not without risks – Computer Weekly revealed earlier this year that the National Cyber Security Centre has, in the past, raised serious security concerns over One Login, and that a security exercise conducted by an external consultancy in March showed that One Login could be hacked without being detected. One Login has also lost its DIATF approval.

DSIT will need to be far more transparent about how it has solved those problems before public trust in the system can be established.

Industry trade association TechUK has called on the government to help address the concerns its announcement has provoked, and to work together to explain the benefits that digital identity can offer the public, citing the “uncertainty for citizens and the private sector alike” that came as a result of Starmer’s announcement.

[Keir Starmer’s announcement] inappropriately positions digital ID as a silver bullet for a multifaceted and nuanced issue, rather than focusing on the benefits that digital ID can actually deliver, meaning its broader benefits are currently missing from the current political narrative TechUK report

“The announcement primarily centred on immigration enforcement, with government linking digital ID to the reduction of illegal working – and without acknowledgement that digital ID solutions, provided under the DIATF, were already being used for this purpose,” said TechUK, in a new report, Digital ID & the UK: Empowering citizens, enabling growth.

“It inappropriately positions digital ID as a silver bullet for a multifaceted and nuanced issue, rather than focusing on the benefits that digital ID can actually deliver, meaning its broader benefits are currently missing from the current political narrative.”

The report added: “Government must work alongside the digital ID sector, civil society, citizens, and other key stakeholders to build public trust, support innovation, and drive adoption. Indeed, the digital ID sector is prepared for a sustained period of engagement, where long-term decisions on digital ID infrastructure, governance, and market design will need to be carefully considered. Clearer communication around future plans is imperative for citizens and the digital ID sector alike.”

There is a path that Starmer and his government could follow, to back away from a badly received proposal and appear to be listening to public concerns, which would promote digital identity as the social and economic benefit it has proved to be in numerous other countries.

It would involve rescinding plans for a “national, mandatory” scheme, in favour of offering the public a wide choice of digital ID apps – both private sector and government-developed – that will enable a mandatory digital right-to-work check to be implemented nationwide. Who knows, maybe it might even have an impact on immigration?

But industry, the public and sceptical MPs alike can only wait and see whether Starmer is politically savvy enough to grasp the opportunity to turn a bad proposal into good policy.

Source

Posted on

MPs press outsourcer TCS over Jaguar cyber attack

MPs have reached out to Indian IT outsourcer Tata Consultancy Services (TCS) seeking answers from CEO Krithi Krithivasan over its alleged involvement in the ongoing cyber attack at Jaguar Land Rover (JLR), which has brought production at the firm to a standstill.

TCS was briefly linked to the Scattered Spider attack on Marks and Spencer (M&S) earlier this year, and did conduct its own investigation into whether or not its systems were the initial source of the incident.

However, in June 2025, the IT giant told shareholders that it had found no TCS systems or users were compromised, and no other customers impacted. A representative for the company said the “purview of the investigation does not include TCS”.

Nevertheless, unconfirmed public speculation has continued to link TCS to other intrusions and attacks conducted by Scattered Spider and associated hacking groups, including incidents at Qantas – a TCS customer – and other airlines.

In the letter, Liam Byrne MP, in his capacity as chair of the cross-bench Business and Trade Committee, said he was trying to find out more information about both the JLR cyber attack and the incidents at M&S and Co-op Group. JLR is coincidentally backed by the wider Tata organisation.

Byrne said the committee was looking to establish more details on TCS’s role as a service provider to all three affected firms – including the scope of services provided to date; whether TCS is conducting or will conduct an internal investigation into the JLR incident; and whether it has conducted or concluded an investigation into the M&S and Co-op incidents and what it found.

Byrne also asked for details of how many UK organisations work with TCS, with a particular emphasis on those working in the 13 sectors that Westminster currently defines as critical national infrastructure, and the total value of services contracts it holds in the UK.

Further steps

On Monday 29 September, JLR said it was “taking further steps” in a “controlled, phased restart” of its manufacturing operations, after receiving a £1.5bn loan guarantee from the government.

“We are informing colleagues, retailers and suppliers that some sections of our manufacturing operations will resume in the coming days,” the firm said. “We continue to work around the clock alongside cyber security specialists, the UK government’s NCSC [National Cyber Security Centre] and law enforcement to ensure our restart is done in a safe and secure manner.”

The crisis has led to production shutdowns across JLR – including at its plants in Brazil, India and Slovakia – and caused a series of cascading effects that are being keenly felt across the UK automotive industry.

As Britain’s largest extant carmaker, JLR is a major force in the wider supply chain, and many smaller companies have had to make cuts of their own in response. According to the Business and Trade Committee, at least one JLR supplier had been forced to sell machinery and other assets. Others have been cutting back on staff hours, leaving thousands of workers out of pocket.

TCS had not responded to a request for comment from Computer Weekly at the time of publication.

Source

Posted on

What Does ‘USB’ Actually Mean? Here’s What It Stands For

Vardanyan Karen/Shutterstock

Chances are high that most of us deal with USB cables at least once a day. Whether that’s because you’re plugging in your phone to charge, or connecting a device to your PC, USBs are a common part of life in our connected and tech-driven world. But have you ever stopped to wonder where USBs came from or even what USB means?

USB is short for Universal Serial Bus. It is an industry standard that was developed by the non-profit USB Implementers Forum, or USB-IF, which is made up of companies that include Microsoft and IBM. The goal was to create a standardized connection type that could provide power and data transfer functionality for components like keyboards, mice, and other devices that connect to personal computers.

Over the years, the types of available USB connectors have evolved, but the connection standard has remained, with ever-increasing adoption helping simplify how you connect and power your devices.

An evolving connection concept

Skrypnykov Dmytro/Shutterstock

Work on the development of USB first began in 1995 when seven companies including DEC, IBM, Microsoft, NEC, Nortel, and Compaq, collaborated to create the connection standard. This group became known as USB-IF, and it introduced the original iteration of USB in 1996. USB was launched as a replacement for various types of interfaces found on devices at the time, including game ports, Apple Desktop Bus ports, and serial ports. It was meant to make connecting devices and peripherals to your personal computer easier, thus helping push adoption of these new PCs.

The development of USB drew off concepts from the serial bus used in the 1979 Atari SIO, as well as from the 8-bit Atari computers and 1980’s Commodore Bus. These concepts were expanded on by an Apple-led consortium with support from other companies, including LG, Sony, Panasonic, Hitachi, Philips Electronics, and Texas Instruments. The USB standard continued to expand, becoming a mainstay for devices across the board, including smartphones, memory flash drives, printers, personal cameras, and webcams.

The rise of USB-C

Javier Zayas Photography/Getty Images

Each evolution of USB has presented faster data and power transfer speeds, with USB 3.0 ushering in signal rates of up to 5 Gigabits per second (Gbit/s) in 2008. This was a massive improvement over the 2000s release of USB 2.0, which only offered a signaling rate of up to 480 Megabits per second. USB 3.1 arrived in 2013, capable of 10 Gbit/s, and USB 3.2 upped that maximum signaling rate to 20 Gbit/s in 2017. Of the differences between USB-C and USB4, one is the speedy 40 Gbit/s performance of USB4, which arrived in 2019. The latest upgrade to the connection standard, USB4 2.0 launched in 2022 with a max rate of 80 Gbit/s.

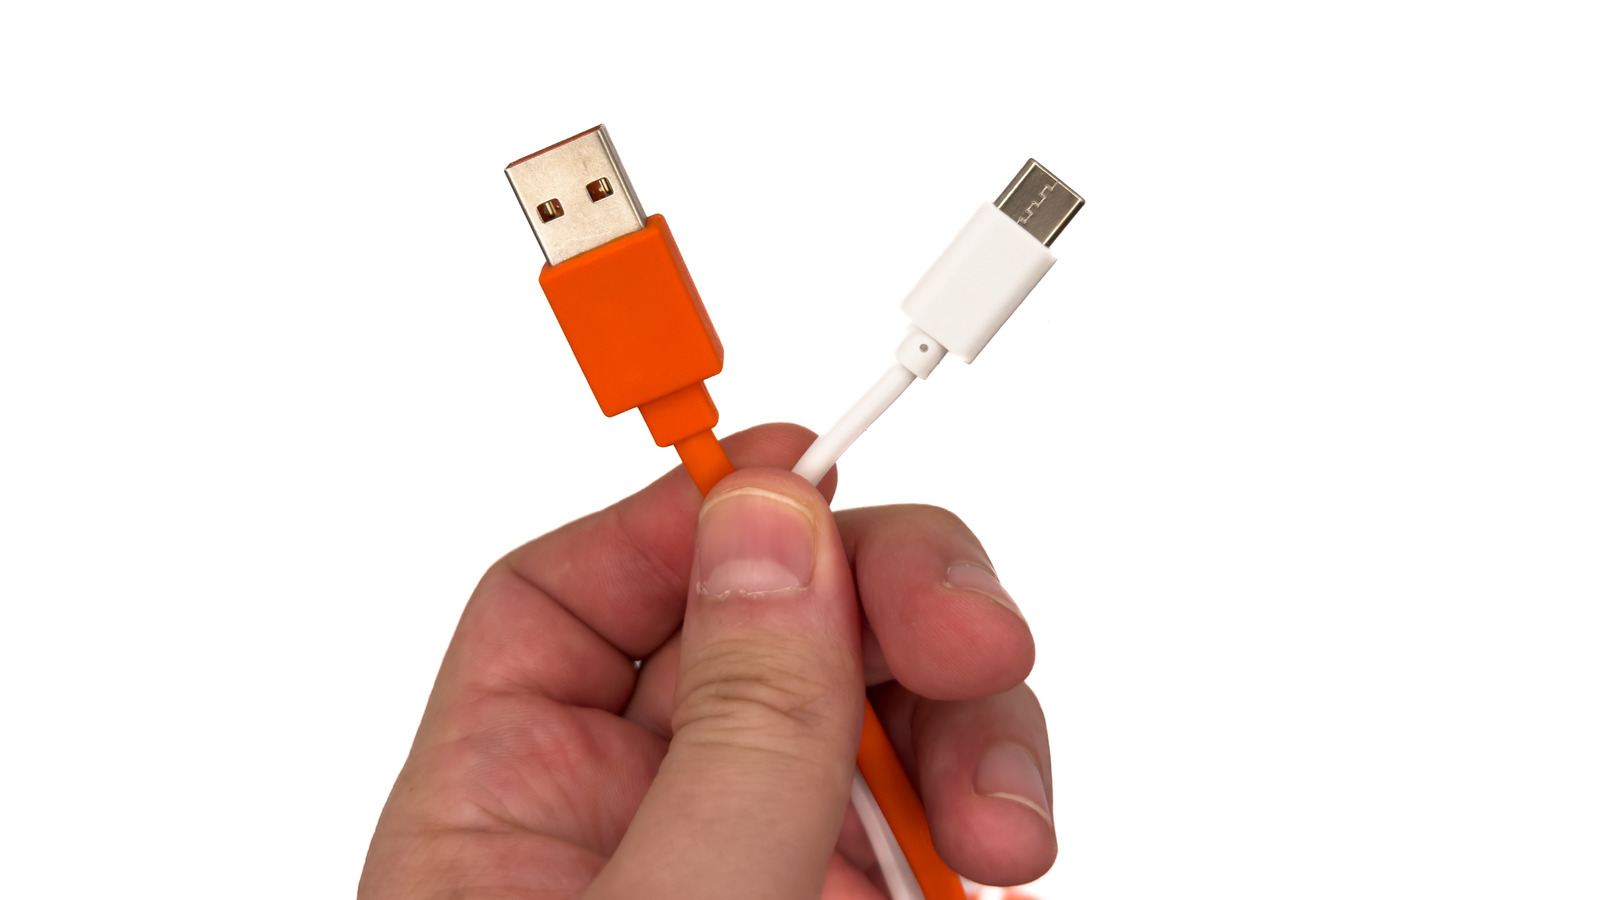
USB originally started as two different main types of connectors — USB-A and USB-B — depending on whether they were upstream or downstream connections. These different connector types can still be found on some devices, and there are other types of connectors that fall under these two hierarchies, including USB Micro and USB Mini.

In recent years, a major update was the introduction of USB-C, an important new connector type that offered both downstream and upstream connectivity. This latest connection type has seen heavy adoption by smartphones, wireless speakers, and other devices. Some of these, like computer displays, have also started to rely on USB-C to deliver power instead of a typical household plug and with the iPhone, the USB-C port is for more than just charging.

Source

Posted on

Zen Internet launches Meraki to deliver SD-WAN portfolio

As businesses increasingly look for ways to harness lower-cost connectivity without compromising on performance, independent broadband provider (altnet) Zen Internet has expanded its enterprise networking portfolio with the launch of Cisco Meraki services.

The company said that its service expansion comes as more altnets expand their fibre footprint, with the offering intended to position the provider as one of the “most complete” software-defined wide-area network (SD-WAN) players in the UK market.

Building on its experience in offering MPLS services, Zen’s Meraki service – spanning LAN, Wi-Fi and SD-WAN – is designed to allow businesses of all sizes to benefit from simpler, cloud-managed networking combined with enterprise-grade security.

Cisco’s Catalyst SD-WAN already caters to enterprises with complex, global operations, but Meraki potentially opens the door to a broader base of customers, particularly mid-sized businesses that may previously have been priced out of advanced networking solutions.

Moreover, by pairing SD-WAN with lower-cost altnet connectivity, Zen said that it promises to help organisations cut costs at a time when IT budgets are under pressure, while still safeguarding against rising cyber threats.

The company said this combination makes its SD-WAN portfolio one of the most flexible in the UK. Larger enterprises can opt for fully integrated, full-stack solutions, while mid-market firms and SMEs can adopt a “lighter-touch” approach by upgrading just Wi-Fi or LAN today, while keeping the option open to move towards SD-WAN in the future.

Zen sees the Meraki launch as not replacing Cisco’s Catalyst SD-WAN but complementing it, giving the ability to support the full spectrum of business needs, from simple, cloud-managed networking through to the most advanced enterprise deployments.

“Security and cost are the two big challenges facing UK businesses right now. By combining the simplicity of Meraki with the security and intelligence of SD-WAN, alongside the cost benefits of our alt-net connectivity footprint, we’re giving customers a genuine choice,” said Jon Nowell, managing director of Zen Business.

“They can modernise their networks without the complexity or expense that has traditionally come with enterprise-grade solutions. Rising cyber crime, coupled with economic uncertainty, is forcing UK firms to seek more for less from their IT investments. At the same time, the shift to hybrid work has increased demand for reliable, secure connectivity across multiple sites. Businesses are no longer asking if they should adopt SD-WAN, but when.”

Aine Rogers, Cisco’s UK&I SME managing director, added: “Businesses across the UK are reimagining how they connect people, places and applications securely to drive better outcomes for all. Cloud-managed solutions like Cisco Meraki enable organisations to boost productivity, improve security posture and reduce IT complexity – all while controlling costs. Through our partnership with Zen, we’re helping businesses achieve faster growth, seamless operations and secure digital transformation – whether modernising a single office or scaling their entire network.”

The launch comes just days after Zen announced that it had expanded its longstanding partnership with business connectivity provider Neos Networks with a major upgrade to 400Gbps connectivity between Manchester and London. Delivered over Neos Networks’ nationwide fibre network, the upgrade to the advanced corridor is designed to support the UK’s growing bandwidth requirements as datacentre investment, AI adoption and full-fibre roll-out increase across the UK.

Source

Posted on

Cato extends zero trust access to SASE platform

The continued surge in hybrid work, bring your own device (BYOD) and contractor reliance has undeniably made businesses more agile and flexible, but it has also introduced a wave of unmanaged devices into enterprise environments that frequently lack security controls, creating exposure to data loss and regulatory risk. To mitigate these issues, Cato Networks has launched Browser Extension, what it calls “a lightweight onramp” to the company’s core secure access service edge (SASE) platform.

Cato cited Verizon’s Data breach incident report, which this year found that 46% of compromised systems containing corporate credentials were unmanaged devices. At the same time, compliance pressures under the General Data Protection Regulation (GDPR), the Health Insurance Portability and Accountability Act (HIPAA), and the Payment Card Industry Data Security Standard (PCI DSS) were continuing to mount. Until now, said Cato, protecting these endpoints meant deploying software IT couldn’t control or forcing users onto enterprise browsers, and that unmanaged devices create risk and compliance pressure for IT leaders.

“Unmanaged and BYOD devices aren’t going away,” said Ofir Agasi, chief product officer at Cato Networks. “They remain the weakest links in enterprise security. Without the safeguards of managed devices, they expose organisations to additional risk.”

Cato also noted that legacy zero trust network access (ZTNA) approaches often require separate tools for different device types. Extending access to unmanaged devices has meant installing new software, such as specialised browsers. The result, said the company, was disruption of the user experience and additional strain on IT operations. 

To address these challenges, Cato has made zero trust for unmanaged devices easy to deploy and simple to maintain. The extension expands Cato’s Universal ZTNA to unmanaged devices – including personal, contractor and BYOD endpoints – without the operational overhead, deployment complexity or user disruption that can come with legacy VPNs or enterprise browsers. It’s designed to simplify secure contractor and BYOD access, unifying zero trust policy management enterprise-wide.

The Cato Browser Extension is a native Google Chrome extension claimed to be able to provide secure access in minutes without requiring client installations or new software. It enforces the same ZTNA policies already applied across the enterprise, so IT doesn’t need to create or manage new rules. And unlike enterprise browsers that force users to adopt a new interface, the extension works natively with standard browsers under one consistent, enterprise-wide ZTNA model. 

With Cato ZTNA, enterprises can unify access across every environment: managed devices connect via the Cato Client, unmanaged devices through the Cato Browser Extension, and sites and branches with a Cato Socket. Every connection is said to be protected by Cato SSE 360 – including Firewall as a Service, Secure Web Gateway, Cloud Access Security Broker, Next Generation Firewall, Data Loss Prevention and Advanced Threat Prevention – ensuring continuous inspection, unified logging and centralised policy enforcement. All platform onramps are said to be unified under one policy model.

With these features, Cato assured that enterprises gain clear strategic advantages in terms of consistent security posture, operational simplicity and audit readiness. That is, businesses can have unified, identity-aware policies across all devices to close security gaps and remove VPNs, enterprise browsers, and point solutions, reducing onboarding time and IT overhead. It also said that firms can simplify audits and meet GDPR, HIPAA, and PCI DSS requirements with consistent enforcement.

In short, Cato believes Browser Extension restores IT control, giving users secure network access while enabling ZTNA for everyone on any device. “The Cato Browser Extension provides customers with the best of both worlds: simple access for users, and complete policy control for IT without adding another tool to manage,” added Agasi.

Source

Posted on

North Wales Police pilots hybrid quantum emergency response

North Wales Police (NWP) has worked with D-Wave on a proof-of-concept hybrid quantum computing application to optimise the placement of police vehicles for emergency response.

The pair reported that the hybrid quantum approach was able to deliver faster, more accurate and more efficient emergency response, allowing NWP to reduce the average incident response time by nearly 50%.

Hybrid quantum computing works like an accelerator, combining the capabilities of quantum computers to solve complex problems with classical computing’s strength in processing logic operations sequentially at scale.

According to D-Wave, the challenge with using classical optimisation technology is that NWP officers need to cover large geographies under difficult constraints and dynamic variables. These include ambitious response-time targets, limited staffing, demanding operational duties, and ever-shifting deployment needs driven by factors such as crime patterns, public events and emergencies.

It is a variation of the travelling salesman problem, which attempts to find the fastest route for a salesman to visit a large number of cities. This is often cited as a task that can be optimised by quantum computing.

But the pilot also takes in other factors, which suggests NWP is also applying predictive analytics to optimise placement of police vehicles – technology that some industry watchers fear can lead to bias and unwarranted profiling of individuals and communities.

Working with D-Wave, NWP tested the use of hybrid quantum computing for “forward deployment”, where officers are placed strategically in high-risk areas to enable faster response times, enhance visibility and deter crime.

D-Wave said the application, which uses a hybrid quantum solver available through D-Wave’s Leap quantum cloud service, outperformed NWP’s classical approach to optimisation by reducing police vehicle coordination time from four months to four minutes, significantly improving real-time adaptability. The test also demonstrated that NWP could respond to at least 90% of incidents within its target response time using the hybrid quantum application.

“Optimising forward deployment is a challenge for most police forces,” said Alistair Hughes, lead for analytics and artificial intelligence at North Wales Police. “A reduction in response time can reduce crime, reduce offence escalation and increase public confidence. We believe D-Wave’s hybrid quantum application could be scaled nationally to save time, reduce costs, improve outcomes and lower our carbon footprint.”

The proof-of-technology project was supported by a grant from the Test and Learn Fund that NWP secured from the UK policing national science and innovation board. Following the successful project, the Office of the Chief Scientific Adviser for Policing recognised it to be of national cross-government departmental interest, with opportunities for future development and deployment. The project highlights the importance and value of cross-border collaboration.

“As police forces increasingly rely on data-driven strategies to improve response times and coverage, hybrid quantum computing can offer the speed, precision and intelligence needed to identify optimal officer placements and enhance public safety,” said Alan Baratz, CEO of D-Wave.

“Hybrid quantum computing is beginning to show real-world potential across private and public sectors, and we’re thrilled to see the potential for it to make a meaningful impact in forward deployment with North Wales Police,” he added.

Source

Posted on

How UK immigration must evolve to attract the best global

As businesses tackle skills shortages and global competition for top talent intensifies, UK immigration policies must do more to actively welcome and retain the world’s best professionals.

Yet the current rhetoric and policy landscape send mixed signals. While the UK government has introduced initiatives to attract skilled workers, entrepreneurs and innovators, high costs and a sometimes unwelcoming tone risk undermining these efforts. For the UK to remain a top destination for global talent, immigration must align more closely with business needs, making the process efficient and genuinely welcoming.

Economic reality and immigration needs 

According to the Tech Nation Unlocking the UK growth potential report 2025, one in three UK founders say availability of top talent is their biggest barrier to growth. In the same report, one in two founders say improving immigration and visa processes would best support their talent needs.

The recent strategic partnership between the US and UK to deliver Europe’s largest AI factory is an ambitious move that underlines the country’s commitment to technological innovation and economic growth. 

Access to talent will play a vital role in supporting such large-scale initiatives. Immigration significantly contributes to addressing labour shortages, especially in industries where domestic talent is either scarce or lacks the necessary expertise. When domestic workers cannot fill vacancies and training initiatives will not fill gaps quickly enough, skilled foreign workers are needed to bridge these gaps and meet business needs.

In the UK, immigration also serves as a significant direct source of revenue for the state. Migrants staying in the UK for six months or more must pay the Immigration Health Surcharge, a fee of around £1,035 per adult applicant per year, intended as a contribution to the NHS. Employers also pay an additional Immigration Skills Charge (ISC), usually £1000 per year of sponsorship, which is expected to rise by 32% this autumn. According to the Office for National Statistics, in Q1 and Q2 2025 alone, the ISC contributed approximately £251 million in revenue to the state.

Current immigration pathways  

To attract top global talent, the government has introduced a range of visa options designed to bring the best and brightest from around the world. The Global Talent visa attracts global leaders in their respective fields. Recognising the strategic economic importance of attracting the world’s best talent, the Prime Minister’s global talent taskforce is reportedly examining proposals to abolish some visa fees for foreign academics and digital experts relocating to the UK. However, this may not help talent pipelines where applicants cannot meet the high bar for the category.

The High Potential Individual visa  is aimed at attracting top international talent to the UK, but is limited to graduates from top-ranked university. Other options include the Graduate visa and Youth Mobility Scheme which allow international students and young people to gain valuable UK experience, building a pipeline of future talent, but both have limitations.

Salary threshold concessions exist for young people and recent graduates under the sponsorship routes. Currently, experienced hire applicants for Skilled Worker visa must receive the higher of £41,700 per annum or the going occupational rate. A new entrant discount means those who qualify must instead meet a lower salary requirement: the higher of £33,400 per annum or 70% of the going rate. 

Challenges and gaps  

Whilst concessions exist for new entrants, Skilled worker salary thresholds remain problematic. After four years, a new entrant must meet the full salary threshold, potentially a 30% pay rise over four years (or two years if time was previously spent on a graduate visa). Salary thresholds are calculated based on the median salary expectation for the role rather than considering the earnings differential of those with five or 20 years of experience, and they do not account for regional salary variation. Concerns exist not only about meeting salaries in the initial application but also about the ability to continue sponsorship at extension.

While work sponsorship follows a clear points-based system, constantly increasing salary thresholds, rising fees and uncertainty over settlement policy reduce the UK’s attractiveness to businesses and individuals looking to establish not only a career, but also a home life. 

Looking ahead 

The UK’s success in attracting and retaining global talent will depend on its ability to balance immigration policy with a business-friendly approach. The goal should be to make the UK not just a place where the world’s top talent want to come, but where they choose to stay, build their career and contribute to a shared future.

Kinka Tonchev is a senior manager at the global immigration law firm Fragomen. 


Source