Posted on

MPs to investigate potential for government digital identity scheme

MPs are to investigate the risks and opportunities of digital identity in the UK, as Labour influencers increasingly call for the introduction of a national scheme.

The House of Commons Home Affairs Committee has announced an inquiry into the issues surrounding the use of government-issued digital ID.

The move comes as the Department for Science, Innovation and Technology (DSIT) prepares to launch its Gov.uk Wallet, backed by a digital driving licence, which citizens will be able to use to help prove their identity and for purchasing age-limited products such as alcohol.

The committee will include other forms of digital identity in its investigation, such as the controversial introduction of eVisas to prove immigration status and the growing use of biometric identification such as fingerprints and facial recognition.

Committee chair Karen Bradley said the inquiry will examine the potential benefits as well as the likely risks.

“Introducing digital ID could help the Home Office achieve its ambitions to reduce crime and improve control over the immigration system,” she said. “But there are also fears that ID schemes could infringe on people’s privacy or be costly to implement effectively.

“The debate around digital ID is growing and we want to find the best evidence for how digital ID could be used by the Home Office to implement its priorities,” said Bradley. “We will be exploring the benefits and risks of digital ID systems as well as the practical challenges to their introduction.”

Written submissions

The committee is inviting written submissions to explore these issues, including whether any government-issued digital identification should be made mandatory.

In April, 42 Labour MPs wrote an open letter to the government calling for a comprehensive digital ID programme.

Earlier this month, think tank Labour Together proposed the introduction of a mandatory national digital identity, which the group labelled as “BritCard”, claiming it would “lay the foundations for a fully-functioning digital identity system that would in time deliver huge benefits in terms of great efficiency and better outcomes in public services”.

The calls from Labour influencers echo those of former prime minister Tony Blair, whose personal think tank, the Tony Blair Institute, has long been a proponent of a national digital identity scheme. When in power, Blair set up a national identity card scheme that was hugely unpopular and eventually scrapped by the coalition government in 2010.

The announcement of the Gov.uk Wallet caused huge concern among the growing number of private sector digital identity providers in the UK, who saw a potential government competitor that could reduce their market opportunity.

However, technology secretary Peter Kyle met with industry players last month and outlined a plan to work in partnership with suppliers, which has – so far – largely quelled those concerns.

The government already has a digital identity system used for access to a growing number of online public services, called Gov.uk One Login. The system, backed by over £330m of funding, has more than six million users, but has recently been dogged by security concerns.

Serious vulnerabilities

In May, Computer Weekly revealed that external security tests found serious vulnerabilities in One Login.

DSIT was also warned by the Cabinet Office in November 2022, and the National Cyber Security Centre in September 2023, that One Login had “serious data protection failings” and “significant shortcomings” in information security that could increase the risk of data breaches and identity theft.

The department said the concerns were “outdated” and arose “when the technology was in its infancy in 2023”.

Public opinion on digital identity is mixed. A YouGov poll suggested that 34% of the public supports the introduction of national identity cards, while 25% strongly support it. However, responses to a 2023 government consultation on data sharing for digital ID found the public expressed strong concerns around data privacy.

A report from Juniper Research into the UK digital ID market predicted a 267% annual growth in the number of people using digital identity apps, reaching 25 million by 2029. Juniper forecasted that more than 45% of UK adults will use the government app – whereas private sector providers will see just 9% growth over the same period.

The Data (Use and Access) Bill, which this week completed its progress through Parliament and awaits royal assent, includes legislation that will help to enable the widespread use of digital identity tools supported by government data.

Source

Posted on

Anker recalls over 1 million power banks after reports of

This week, accessory maker Anker announced one of its most sweeping recalls to date. Due to a series of incidents resulting in fires, explosions, and minor burn injuries, Anker is recalling 1.1 million PowerCore 10000 power banks with model number A1263.

Anker recalls PowerCore 10000 power banks

Anker says affected models were manufactured between January 1st, 2016, and October 30th, 2019, and sold between June 1st, 2016, and December 31st, 2022. The company explains that there is a potential issue with the lithium-ion batteries in these power banks that causes them to overheat, leading to melting plastic, smoke, and fire hazards.

According to the U.S. Consumer Product Safety Commission, the recall was officially issued on June 12th, 2025, and affects around 1,158,000 units in all. Prior to the recall, Anker received 19 reports of fires and explosions caused by the power banks, resulting in two minor burn injuries and 11 instances of property damage totaling over $60,700.

The PowerCore 10000 recall comes just six months after Anker recalled thousands of Bluetooth speakers due similar concerns revolving around lithium-ion batteries.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

What to do if you have a recalled power bank

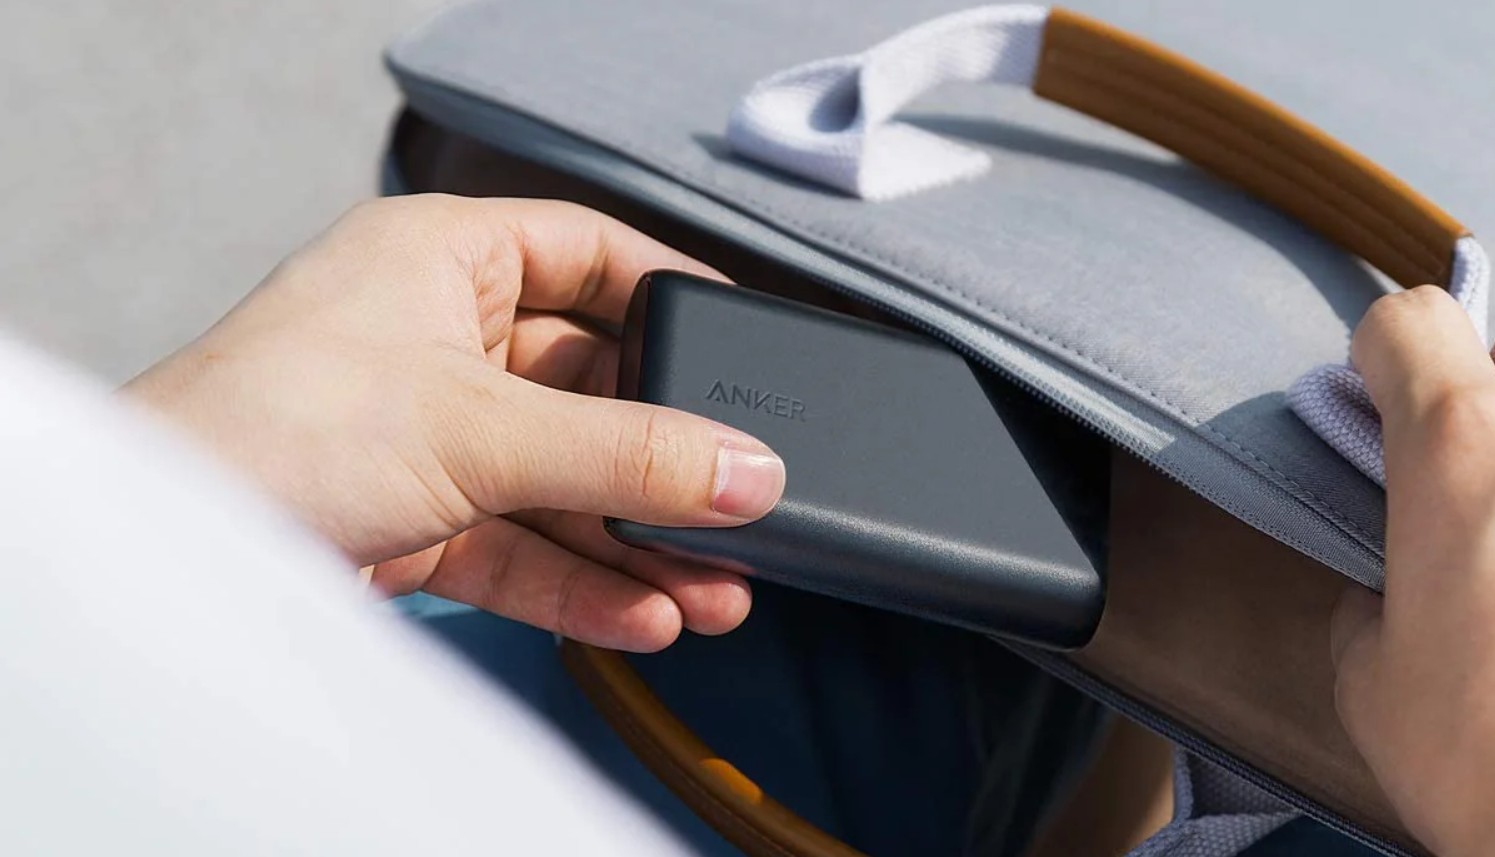
If you own an Anker power bank, we’d recommend checking and make sure it isn’t an affected model. Once you have the PowerCore 10000 power bank in hand, find the product information on the side of the device. You’ll find a model number in the upper-left corner. If it says “A1263,” it’s part of the recall and needs to be properly disposed of.

How to find the model number on a PowerCore 10000. Image source: Anker

The next step is to fill out Anker’s recall form. You’ll need to provide proof of purchase, product details, and photos of the device. If Anker confirms your power bank is part of its recalled batch, you’ll be able to choose between a $30 Anker gift card or a new, free power bank from Anker to replace the fire hazard currently sitting in your home.

At this point, you’re free to dispose of your power bank. Here’s how to do so safely:

Do not throw this recalled lithium-ion battery in the trash, in the general recycling stream (e.g., street-level or curbside recycling bins), or in used battery recycling boxes found at various retail and home improvement stores. Recalled lithium-ion batteries must be disposed of differently than other batteries, because they present a greater risk of fire. Your municipal household hazardous waste (HHW) collection center may accept this recalled lithium-ion battery for disposal. Before taking your battery to a HHW collection center, contact it ahead of time and ask whether it accepts recalled lithium-ion batteries. If it does not, contact your municipality for further guidance.

Once again, if you think there might be an Anker power bank sitting in a drawer somewhere in your house, it’s probably worth checking to make sure it’s not this one.

Source

Posted on

Apple encryption row: Does law enforcement need to use Technical

How far are criminal investigations inhibited by the wide availability of end-to-end encryption (E2E)?

The Home Office and UK law enforcement agencies think the problem is urgent, hence the politically tricky decision to use a little-known feature of the Investigatory Powers legislation – the Technical Capability Notice – to seek to impose back-door conditions on Apple’s Advanced Data Protection (ADP) system. Most observers see this as a test case for future control over many other E2E services such as WhatsApp, Facebook Messenger, Signal and Telegram.

 But an examination of some recent high-profile cases show that successful prosecutions are possible even where apparently robust end-to-end encryption (E2E) has been deployed by suspects. What needs to be understood is that E2E communications are often only one element in a possible criminal enterprise and that other traces of criminal activity can be found by conventional investigatory techniques. 

 Moreover elsewhere in the Investigatory Powers Act (IPA) 2016 is the ability to obtain warrants to hack – referred to as Equipment Interference. Where end-to-end encryption is deployed, encryption and decryption only take place on the smartphone handset or a computer rendering data traffic unreadable even by Apple or WhatsApp and other service providers. But if you can hack the device remotely to read its contents those contents will be viewable unencrypted.

 Operation Venetic

 This is what happened in the National Crime Agency’s to date biggest investigation, Operation Venetic. The handsets in question, called EncroChat, used a variety of anti-surveillance techniques which for a while between 2016 and 2020 gave their customers, many of them involved in serious organised crime, the illusion of safety from scrutiny. E2E was used for handset-to-handset communications. The phones themselves were highly resistant to conventional forensic examination, even when seized.

The break-through technique was developed by the Dutch and French with the French in operational control and consisted of using a “tool” or “implant” to hack. The tool was uploaded covertly and enabled covert data exfiltration. Legally it fell into the category of Targeted Equipment Interference under Part 5, IPA 2016.

 Between April and mid-June 2020 vast quantities of messages and photos were downloaded and the UK-related ones ended up as evidence in UK trials. Defence lawyers and experts mounted a number of vigorous objections to the admissibility and reliability of the Venetic evidence but in the end in nearly all cases the product was admitted and in the words of the NCA, thousands of conspiracies involving wholesaling of narcotics and murder were successfully penetrated.

Covert hacking tools

There is no serious shortage of “tools” available to law enforcement to achieve covert hacking.   Among such tools that have been identified are Pegasus from the Israeli NSO Group, Hermit, Graphite and Predator. Within the Snowden files, now over 11 years old, are references to Tailored Access Operations. It is a reasonable assumption that there are other such tools which have avoided publicity.

But there were many successful prosecutions of serious criminal activity before the Dutch/French intervention. Suspects were found in possession of EncroChat phones – their contents could not be read but there was enough evidence available by conventional means.

 I acted as a prosecution expert in many of these cases brought by the NCA and Regional Organised Crime Units (ROCUs). They included Operations Tradite, Meropia, Clubman, Hammer, Sparkle and others. My role was as a supplement to already well-researched investigations – to describe the known functions of the phones and to point to their very high cost – £1500 outlay and £800 to renew after 6 months. I must have considered over 100 such phones.

Other sources of evidence

So what were the ingredients of those successful pre-Venetic EncroChat cases? Among them, simple observation of people with apparently suspiciously excessive lifestyles, open source intelligence of social media, informants, formal directed surveillance, CHIS (covert human intelligence sources), CCTV both public and private and information from other investigations. 

Once there was reasonable suspicion, warrants could be obtained for communications data. Encrophones could only communicate with other Encrophones so that everyone that had one also had a regular smartphone.

Communications data shows who is in contact with whom to discover conspiracies plus the geo-movements of the phone’s owner which might reveal county lines of drug distribution via cellsite analysis.

Financial records could be obtained. The activity of identified vehicles could be tracked by ANPR (automatic number plate recognition). In suitable circumstances a “property interference” warrant enabled audio and video bugs to be placed in buildings and vehicles. 

 Equipment Interference

 According to the Investigatory Powers Commissioners Office (IPCO), some 1100 equipment interference warrants have been issued to law enforcement annually, though most of these do not produce admitted evidence as the authorities have sought public interest immunity (PII) certificates to prevent their disclosure.

 Also possible, though only usable for intelligence not evidence, were warrants for interception of traffic in transmission.  Finally, as an investigation reached a crescendo – premises searches might produce drugs paraphernalia, weaponry, untoward quantities of cash and unfortunate items of literature.

 A particularly important ingredient has been the use of link analysis software which combines and visualises all these separate strands of evidence. They are great for investigators but also useful to produce court exhibits to show to juries.

 Examples are available from Chorus, I2, Cambridge Intelligence and others. Similar techniques can be and are used in terrorist cases and against paedophile rings.  In cybercrime and IP piracy cases “communications data” can also include IP addresses and logging activity.

 All of these techniques present few of the political challenges faced by the Home Office’s attempt to bring into the definition of the Technical Capability Notice the attempt to “break” strong encryption.

 The political challenges include the risks of weakening the legitimate use of encryption in e-commerce, online banking, health records and compliance with data protection legislation. And, more recently, US sovereign objections to UK law enforcement issuing broad-based orders to major US companies.

Professor Peter Sommer is a digital evidence expert witness

Source

Posted on

Cisco Live 2025: The digital workplace gets closer to ‘distance

More than five years after Covid-19 induced a massive shift in working practices, businesses are still actively refining their hybrid work and return-to-office strategies, meaning they are required to balance employee satisfaction and retention with critical business priorities such as productivity, operational efficiency and profitability, according to research from Cisco.

Released during the Cisco Live 2025 conference, the Navigating hybrid work strategies in evolving workplaces study was based on a double-blind survey, undertaken in April 2025, of 21,513 employers and employees in full-time roles across 21 global markets in industries ranging from financial services to healthcare and manufacturing. Respondents were segmented based on the level of their promotions and pay rises into three groups: high performers, average performers and low performers.

Among the fundamental findings are that at a time when many organisational leaders are encouraging or mandating their teams to spend more time in the office, “significant” disconnects are appearing between employer expectations and employee preferences.

It also highlights the vital relationship between workplace flexibility and overall well-being, and the necessity for transparent communication around the growing number of return-to-office policies.

As it released the findings of the report, Cisco noted that compared with its inaugural global hybrid work study in 2022, Employees are ready for the future of hybrid work, are you?, there was a clear global trend towards increased in-office work, with the percentage of respondents with hybrid work arrangements decreasing from 62% in 2022 to 45% in 2025.

In addition, current work-from-office arrangements were found to be making significant improvements to well-being – in particular socially and emotionally. Cisco suggested that over time, employers have become more adept at tailoring hybrid work arrangements to better support employees’ needs.

Yet as working practices returned towards more time in the office, leaders were also seen to be facing critical challenges with communicating changes and the need to manage and balance the various expectation gaps that exist.

Engaging employees

Indeed, the data is said to reveal a significant area for improvement for leaders engaging employees in the decision-making process around hybrid working arrangements. Principally, that involves communicating these changes when they occur, and justifying the business case for them.

The study also shows that hybrid working arrangements continue to remain an effective tool in the war for talent acquisition and retention. Notably, 63% of all respondents said they would accept a pay cut for the option to work remotely more often. Nearly three-quarters of all workers reported higher productivity under their new working arrangements.

Regarding segmentation of employees, half of high performers were found to be working at companies requiring less than three days in the office per week. In addition, this group preferred remote work while also recognising the importance of collaborative office spaces.

With hybrid arrangements now a firm feature of the modern workplace, collaboration technology was seen by both employers and employees as crucial for enabling better engagement and more flexibility. Investment was already occurring in this area. The survey also revealed that less than half (49%) of employees believe their organisation provides a “seamless” workflow experience across all work locations.

The study concluded with seven calls to action: navigate varying views of the workforce; flexibility is non-negotiable and drives performance; trust must be built to optimise productivity; clear communication is key; encourage a balance of flexibility and office presence; design policies for today and the future; and future-proof workplace technology offerings.

Future-proofing workplace technology services was identified as crucial by the vast majority of employers in the survey. As many as 93% noted the intrinsic importance of collaboration tools (93%) and employees (90%), and investment in AI is widespread. However, the current reality is that only 49% of employees feel workflows are seamless across all work locations. This, said Cisco, underscored the need for better technology devices and capabilities to provide a superior and more seamless employees experience.

At the conference, Jeetu Patel, Cisco president and chief product officer of AI, argued that the company’s products were now beginning to make a difference in terms of bringing people closer and making better connections, coming from the principle of “distance zero”. “When people are on a call, we should make sure that the distance between those two people goes away, that they feel like they’re there with each other,” he said. “When you are in a [meeting] room and there are other people who you’re collaborating with who are not there, it should feel like you’re all in the same place. That’s one example of how technology is helping deliver [a superior] experience.

“But it goes back to a hierarchy of needs,” added Patel. “At the at the very core level, you need basic tools to get your work done. But if you are going to come into the office to be around other people and do creative work with your team, there are other needs that technology can solve. For example, helping you find a conference room, helping you find a desk to sit next to your coworkers. Coming back to AI adoption, I think you can just look at the tool itself, and you start thinking about the process, and you start thinking about the whole workflow, and this is where it becomes a team sport.”

Moving from team sports to Teams, Patel added that the Microsoft unified communications system would run natively on the Cisco range of Webex collaboration devices in the same way its own system would. He noted that a number of major organisations had standardised Microsoft Teams rooms and achieved standardisation on Webex devices. More significantly, the devices’ switches and cameras were augmented into the Webex portfolio to become de facto sensors on an office network, providing data about facilities and campuses, offering temperatures, air quality and occupancy so that a working environment and workplace can be more effective and managed in an easier way.

“We want to make sure that that distance zero, which is an end user-focused concept, also brings in the IT administrator,” he said. “We wanted to have one-click distance zero for the IT administrator, and we did this last year with the microphone, where [with] one click, you can just easily configure. Just plug it into a switch and it auto-configures itself. You don’t have to do anything.”

This capability has now been rolled out to video and cameras configured to provide cinematic-quality meetings to improve engagement. Explaining the rationale for the move, Patel asked why it was harder to be in a video conference for an hour than watch a movie that ran for maybe twice as long.

“Why is that? Because in a movie, your frame speeds are changing, and so it actually resets your brain … but in a video call, you’re just looking at the same angle for the full hour,” he said. “If you have a conference with multiple people, all their cameras auto-configure, and they work with each other and they give you a cinematic quality of the media. If someone is speaking, they’ll give you a close-up … and if you get zoomed out, it’s automatically going to do that.”

Headset integration

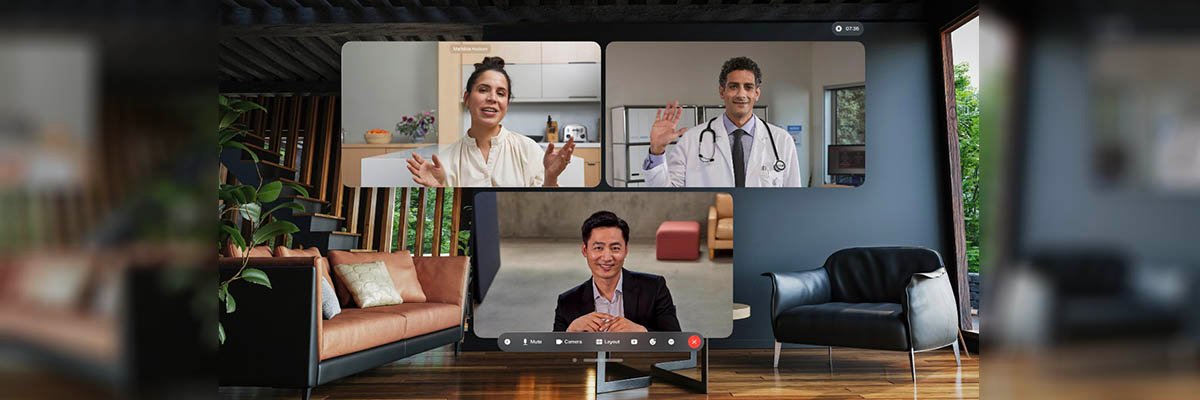
The Webex video conference ante has been upped considerably through integration with the Apple Vision Pro headset so that users can experience a spatial meeting. Cisco first revealed in February 2024 a roadmap to support the next age of collaboration, which will lean on technology partnerships with firms such as Nvidia and Apple, in the latter case realising the potential of its recently launched Vison Pro device for the Webex collaboration service.

In setup at Cisco Live, the Apple device was deployed to test use cases based on a standard Webex app – alternatively in a Microsoft Teams room mode – with a Cisco room bar Pro sound system.

From there, anything standard ends and what is experienced is not a traditional meeting room. What is delivered using the Apple device is high-resolution stereoscopic video, and a spatial studio of sorts, whereby somebody can present or show a product or process in high-resolution 3D.

Describing what was possible with the headset and the app, the Webex team said Apple was currently in an “inspirational phase”, and that the two companies were working “hand in glove” to show “the art of the possible” from a spatial configuration, spatial perspective and spatial desktop. In addition, an increasing number of Apple developers were involved in spatial technology projects such as physical training, representation of diagrams, and – as shown at Cisco Live 2025 – real 3D models of objects that could be appreciated better from being part of a virtual meeting experience.

Apart from the basic 3D capability, another key part of the visual experience regards the user interface. In the 3D session, contributors’ individual video feeds can be bought out from the traditional multiple user screen view and isolated anywhere in the 3D viewing sphere. In addition, there’s a general volumetric 3D view that can be activated to provide depth.

Again, the key is distance zero, offering experiences with much better depth, more realistic colours, and a more realistic in-person experience than with the standard Webex. As the Cisco Live team said: “You have the ability to take the distance out of ‘conferences’, and it looks and feels like you’re in there. When you see something in a flat 2D screen, their eyes aren’t really even intended to be looking at you for extended periods of time … In terms of optics, our muscles and nerves are not meant to see that. Yet sitting here looking in full 3D, we can be here for hours looking at each other and everybody in the room.”

This room is intended for a variety of use cases – including product design; engineering; education and training; healthcare; and oil and gas exploration – anything that can be improved from a true spatial experience.

Source

Posted on

AI Summit London: Managing legacy IT and the pace of

Panel members on the AI as a Competitive Advantage session held at the AI Summit in London this week discussed the reality businesses face when trying to move artificial intelligence projects into production.

Data presented in the Summit’s AI at Scale stream, suggests that 80% of proof-of-concept AI projects fail to move into production. While the panel discussion did not focus heavily on moving beyond AI proof-of-concept projects, as that topic was discussed in a previous session, two members of the panel did raise the issue of how AI aligns with enterprise IT.

This can be a challenge for moving beyond proof of concepts, especially when the new technology being piloted needs to integrate with existing IT infrastructure and enterprise datasets.

Ravi Rabheru, head of AI centre of excellence at Intel for EMEA, noted that the big challenge businesses face is around technical debt.

Dara Sosulski, head of AI and model management for HSBC, added: “The bigger the company, the more the technical debt and the more the complexity.”

It is an area of concern both in large enterprises and in government, which has an agenda to push AI-enablement across the public sector. The Public Account Committee’s (PAC’s) Use of AI in government report from March 2025 noted that AI relies on high-quality data to learn. However, the committee was told by the Department for Science, Innovation and Technology (DSIT) that government data is often of poor quality and locked away in out-of-date legacy IT systems.

Sosulski noted that IT leaders need to assess whether their data infrastructure is right for AI applications to prioritise and understand what is achievable: “Infrastructure is the thing that unlocks the keys of the Kingdom, in a way. You then have something that is a backbone and it’s modular and interoperable. [With such IT infrastructure], you can access applications from other places and you can connect to other things.” 

However, she acknowledged that it may not be possible to provide a date as to when all the components needed for AI will be in place in some organisations.

Build or buy?

But the industry is keen to promote the value of ready-made AI capabilities. Sosulski believes that the build-versus-buy question essentially comes down to the use cases the business wants to tackle, saying: “I think all enterprises have now adopted a very similar set of tools to solve problems like software development, drafting emails, translating a document and document Q&A.”

Given that there are products that cater for such use cases, she added: “There are some use cases that are so generalist, we would consider them core capabilities. Those are ones that we consider buying as an enterprise wide solution that is tested and integrates well with our other IT infrastructure. Everybody realises you don’t solve them internally at great expense.” 

While business and leaders tackle technical debt and balance when to build and when to buy AI functionality, they also need to keep abreast of the latest developments.

While the whole tech industry appears to be steamrolling agentic AI and artificial general intelligence (AGI), Sosulski recommended that technology decision-makers look at what developments are relevant to the business.

Sosulski felt that there’s less of a need to keep up with the latest AI foundation model. “Despite everything changing constantly, a lot of these models wind up being a much of a muchness for what you want to do,” she said. “We don’t need new foundation models every six months. HSBC and most companies are that way and so, at some point, you just get familiar with the ins and outs of what the models can and can’t do.” 

With a selection of some open source and proprietary models, Sosulski urged delegates to focus on assessing which models work best for their use cases. These can then be piloted in proof-of-concept projects to prove they work. She also recommended putting in a place a control framework and IT infrastructure that enables retraining and iterating quickly.

With such a setup, she said: “You can keep moving things out into production without having to overhaul everything every six or 12 months.”

Source

Posted on

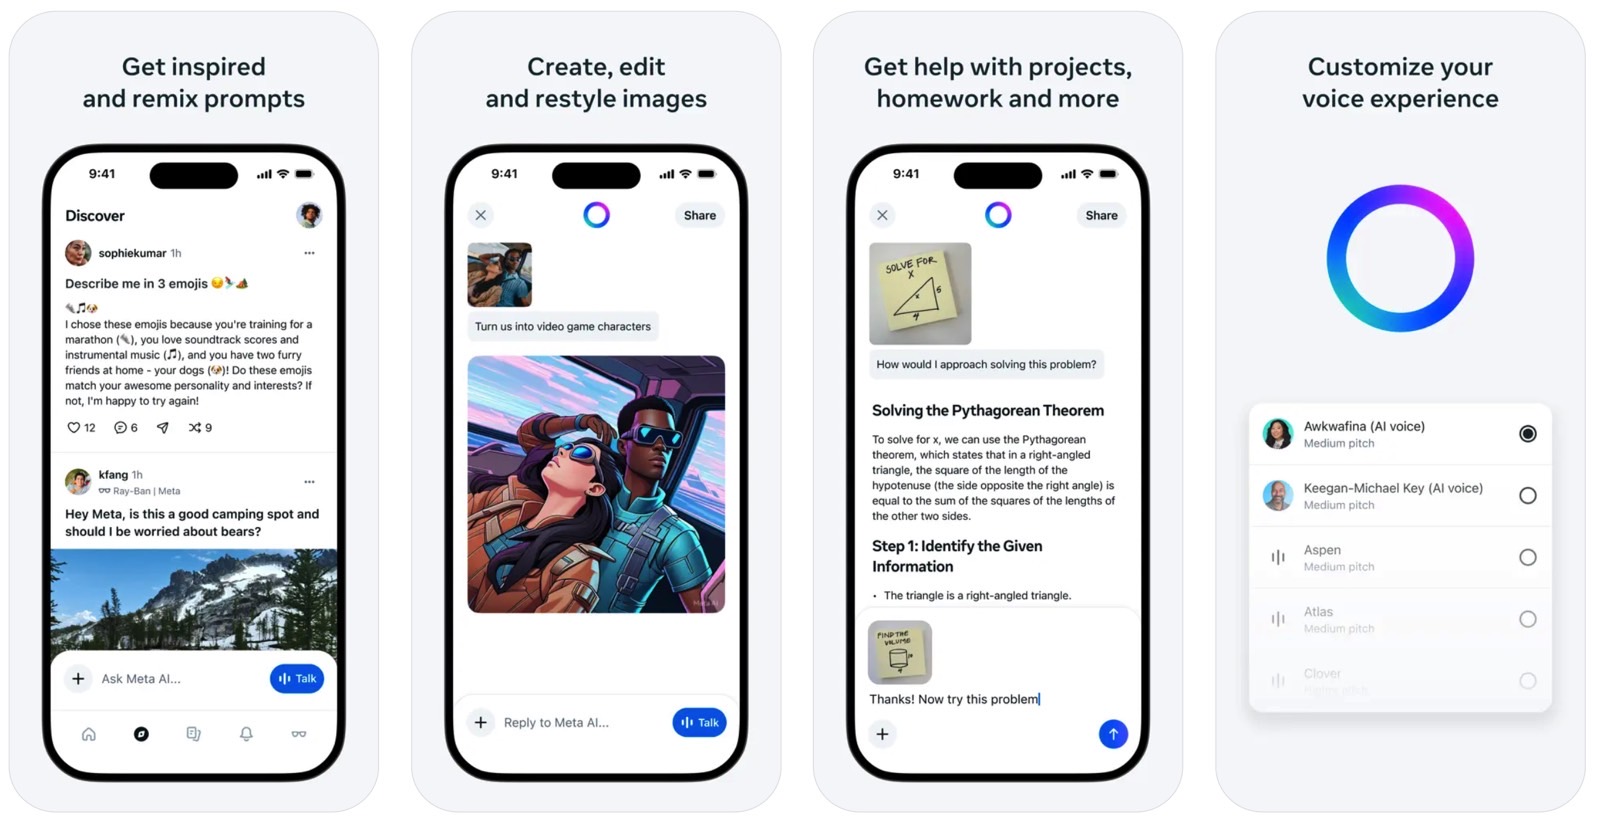
The Meta AI app is currently going viral for all

Meta launched the Meta AI app in late April to take on ChatGPT and other chatbots. Unlike rival apps, Meta AI comes with social features that nobody asked for. But Meta’s desire for Meta AI users to share their chats with others via a social feed isn’t surprising. Social media is how Meta makes its money. All of its apps are social apps. Also, bringing a social element to an AI chatbot experience could always work in Meta’s favor.

However, that’s hardly the case right now. Meta AI has gone viral this week for a huge issue. Rather than discussing a unique Meta AI feature that makes the chatbot a must-have AI product, people are talking about the wildly inappropriate chats that take place on the platform, which some users are sharing online by mistake for others to see.

Sharing AI chats is optional, but it looks like plenty of users don’t realize what they’re doing, or they don’t care. Whatever the case, the Meta AI chats that appeared on social media are deeply disturbing. They show what can go wrong if an AI firm working on frontier AI experiences doesn’t handle user privacy correctly. Meta could do a better job informing users that the “Share” button will move the Meta AI chat to the Discover feed.

According to TechCrunch, around 6.5 million people installed the standalone Meta AI app. The figures come from Appfigures, not Meta. That’s hardly the user base that a company like Meta can brag about. Meta AI is a standalone app. It wasn’t embedded in a more popular app like Instagram or WhatsApp, so it’s up to users to install it.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

Before rolling the app out, Meta largely focused on forcing Meta AI experiences into all its social apps, including WhatsApp, Messenger, Instagram, and Facebook. That’s why Meta can say Meta AI has 1 billion monthly users.

The standalone Meta AI app has yet to achieve such reach. But even so, 6.5 million isn’t a small number. It shows that some people are genuinely interested in the Meta AI chatbot experience. However, not all of them know how to protect their privacy.

I haven’t tried Meta AI, nor am I likely to get on the app anytime soon. But privacy is one of my main concerns when it comes to AI products. Meta could do a better job here. While I haven’t been exposed to private Meta AI chats that were shared online by users who don’t know (or care) about how the social aspect works, there are plenty of examples.

Here’s a take from TechCrunch:

Flatulence-related inquiries are the least of Meta’s problems. On the Meta AI app, I have seen people ask for help with tax evasion, if their family members would be arrested for their proximity to white-collar crimes, or how to write a character reference letter for an employee facing legal troubles, with that person’s first and last name included. Others, like security expert Rachel Tobac, found examples of people’s home addresses and sensitive court details, among other private information.

It keeps going, too. Here’s what Gizmodo found in the Discover feed, which is where the Meta AI chats go if you don’t know what you’re doing and press the Share button:

In my exploration of the app, I found seemingly confidential prompts addressing doubts/issues with significant others, including one woman questioning whether her male partner is truly a feminist. I also uncovered a self-identified 66-year-old man asking where he can find women who are interested in “older men,” and just a few hours later, inquiring about transgender women in Thailand.

Andreessen Horowitz partner Justine Moore posted screenshots of Meta AI chats in the Discover feed, summarizing some of what she saw in an hour of browsing:

  • Medical and tax records
  • Private details on court cases
  • Draft apology letters for crimes
  • Home addresses
  • Confessions of affairs…and much more!

None of these topics should be broached in your conversations with any AI model, whether it’s Meta AI, ChatGPT, or any of the other countless startups.

What you can do

If you or someone you love is using Meta AI, you should ensure the privacy settings are set correctly. Gizmodo, which hilariously advises users to get their parents off of Meta AI, lists the steps needed to prevent Meta AI chats from making it to the Discover feed:

  1. Tap your profile icon at the top right.
  2. Tap “Data & Privacy” under “App settings.”
  3. Tap “Manage your information.”
  4. Then, tap “Make all your prompts visible to only you.”
  5. If you’ve already posted publicly and want to remove those posts, you can also tap “Delete all prompts.”

Also, don’t tap the Share button if you want to keep an AI conversation private. As TechCrunch and Justine Moore point out, the Meta AI chats are not public by default. But some people press the Share button in chats, unaware they’re sharing them with everyone else on the platform.

I’ll also remind you that Meta will use all your posts shared on its social networks to train AI. You might want to opt out of that if you haven’t done so already. And if you don’t want Meta AI to use any of that public information for more personalized responses, you’ll want to opt out of that too.

Finally, remember that it’s not just older, less tech-savvy people using Meta AI in ways that might be inappropriate. You’ll want to check on your teens as well and see what sort of chats they might have with Meta AI.

Source

Posted on

VodafoneThree begins operation with 5G SA, broadband push

Two years after the merger of the two leading UK connectivity companies completed, VodafoneThree is now set to challenge the mobile arena and the UK’s broadband market by aiming to cover all homes with fibre or fibre-like speeds, boosting this ambition with a new partnership with Community Fibre.

Vodafone and Three first announced plans to merge in June 2023 and the new combined business will operate under the VodafoneThree brand, with 51% owned by Vodafone Group and 49% by CK Hutchison Group Telecom (CKHGT) Holdings. Vodafone will fully consolidate VodafoneThree in its financial results and the company’s CEO will be Max Taylor, who currently leads Vodafone UK. Three UK’s Darren Purkis has been appointed chief financial officer (CFO).

Backed by an £11bn infrastructure investment – one of the key guarantees by the two companies to gain closure of the deal from UK regulatory authorities – to connect all four nations and every community, VodafoneThree will be the biggest mobile network operator in the UK, with 27 million customers.

In addition, it said that it is the only UK operator with a quarter-by-quarter, year-by-year, guaranteed plan to reach 99.95% 5G Standalone (5G SA) population coverage by 2034. The 5G SA network build-out plan is front-loaded so that it will hit 90% population coverage from a current baseline of 47% by the end of the third year.

VodafoneThree assured that up to 50 million people will have access to its fastest 5G speeds in just one year. Explaining why it is emphasising 5G SA, the company said only such networks will have the capacity and speed to manage the vast amounts of data that applications such as AI will require, meaning that the target is to build the first nationwide, AI-ready network.

The new merged company will operate a multi-brand mobile strategy in consumer with Vodafone, Three, VOXI, Smarty and Talkmobile remaining, while Vodafone will be the only brand for business customers, with one team able to tailor systems to a customer’s needs, with the ambition to become the UK’s biggest converged network for business.

Over the course of the next 12 months, VodafoneThree will bring Three’s fixed wireless access services together with Vodafone’s full-fibre offer into one home broadband portfolio under the Vodafone brand. There will only be one converged brand for both businesses and consumers.

Through the sharing of combined spectrum, VodafoneThree said that within two weeks, seven million Three and Smarty customers will receive a 4G boost, with an improvement in 4G data speed of up to 20%. Within a few months, all legacy Vodafone and Three mobile customers will gain access to roam on each other’s networks at no extra cost.

This is intended to remove a total of 16,500 sq/km of “not spots” – said to be equivalent to 10x the size of London – by the end of the 2025, with the first sites already having been turned on. Taking advantage of Vodafone’s recent partnership with AST Space Mobile, VodafoneThree said that it will launch beta trials on a “first-of-its-kind”, space-based satellite mobile network by June 2026. The space communications platform will complement the existing network build, eliminating coverage gaps in places that otherwise couldn’t be reached.

While much of the merger focus has been on mobile, VodafoneThree said that it will challenge the broadband market, bringing better value and choice through existing and new partnerships. The new company boasts more than million customers and can currently bring fibre or fibre-like speeds of up to 2.2Gbps to 22.5 million homes and businesses.

The merger has attracted support from across the communications industry and from the world of politics. Commenting on what it could achieve, chancellor of the exchequer Rachel Reeves, said: “I’m delighted that that this huge investment is being made in mobile phone network infrastructure, better connecting people with families, loved ones and work by providing stronger, more widespread 5G coverage.

“Our Spending Review is all about growing our economy and attracting private investment to deliver on our Plan for Change, and it’s fantastic that VodafoneThree have chosen to join us on our mission of national renewal.”

Source

Posted on

When will Apple release the first iOS 26 public beta?

With WWDC 2025 behind us, developers are now testing the first iOS 26 beta. Meanwhile, many iPhone owners are wondering when they will have a chance to preview the upcoming features. Here’s everything you need to know about the availability of the iOS 26 public beta.

Did Apple announce when users will be able to download the iOS 26 public beta?

Yes, Apple’s CEO Tim Cook announced during the WWDC 2025 keynote that the public beta of iOS 26 will be available in July. Apple usually releases a few betas exclusively for developers before opening up beta testing to the general public.

When should you expect the first public beta?

We expect to see iOS 26 public beta 1 between the second and third week of July. Here’s when Apple released the first public beta of previous iOS updates in the past few years:

  • iOS 15: June 30, 2021 
  • iOS 16: July 11, 2022 
  • iOS 17: July 12, 2023
  • iOS 18: July 15, 2024 

We wouldn’t be surprised if the public beta of iOS 26 was released around July 14 or July 15.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

How can you enroll in the beta program?

If you want to be one of the first to try the public beta, you need to enroll your Apple Account in the Apple Beta Software Program. Here are the steps to follow:

  • First, make sure you’re enrolled in the Apple Beta Software Program
  • On your iPhone, open the Settings app
  • Tap on General, and then Software Update
  • Tap on Beta Updates and enable iOS 26 Public Beta

These are some of the features you should expect to see on iOS 26 public beta 1

Image source: José Adorno for bGR

Once the public beta is available, you’ll be able to try out the following features:

  • All-new design: Apple offers a brand new design with the Liquid Glass UI. It’s a drastic change from the previous design language of iOS 18.
  • Messages app improvements: Users can screen messages from unknown senders, create polls, and generate unique backgrounds with Image Playground.
  • Apple Music: Alongside a revamped app, users can pin favorite songs on top of the library, in addition to several other changes.
  • ChatGPT improvements: ChatGPT features onscreen awareness for those who use it to power Apple Intelligence.
  • Genmoji and Image Playground updates: Apple says iOS 26 improves these OG Apple Intelligence features as it’s now possible to mix emoji, Genmoji, and descriptions together to create something new.

Supported devices

Notch on the iPhone 16e. Image source: Christian de Looper for BGR

These are all of the devices that will support iOS 26:

  • iPhone 11
  • iPhone 11 Pro and 11 Pro Max
  • iPhone SE (2nd gen)
  • iPhone 12 mini and iPhone 12
  • iPhone 12 Pro and iPhone 12 Pro Max
  • iPhone 13 mini and iPhone 13
  • iPhone 13 Pro and iPhone 13 Pro Max
  • iPhone SE (3rd gen)
  • iPhone 14 and iPhone 14 Plus
  • iPhone 14 Pro and iPhone 14 Pro Max
  • iPhone 15 and iPhone 15 Plus
  • iPhone 15 Pro and iPhone 15 Pro Max
  • iPhone 16 and iPhone 16 Plus
  • iPhone 16 Pro and iPhone 16 Pro Max
  • iPhone 16e

Below, you can learn more about some of the other new features coming in iOS 26.

Source

Posted on

How Meta tracked your mobile browsing on Android without consent

If you visited adult sites on your Android device via incognito browsing sessions or a VPN while also logged into Facebook and Instagram, Meta might know about it. Not only that, Meta might know what you watched, what you clicked, and what you bought.

Regardless of what you were doing on your device, if you did it on an Android phone while logged into Meta’s social networks, Meta was likely tracking it.

What will Meta do with all that extra data it collects about you? It’ll use the data to serve personalized ads that match your most recent interests.

The method Meta used is incredibly abusive, as the company did it without obtaining consent from the user. Instead, Meta used Android browsers to link browsing history to Facebook and Instagram profiles. Even Google, which has its own history of tracking users without consent, called the procedure a “blatant violation” of its security principles.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

Meta stopped the tracking this week, but even if it were to continue, Google is already patching Chrome. I wouldn’t be surprised to see regulators investigate Meta’s behavior next, especially in jurisdictions like the EU, which have stronger privacy protections for users.

Meta’s abuse was discovered accidentally by professor Günes Acar from Radboud University in the Netherlands (here’s his research). He observed an unexpected connection between a page containing trackers, including Facebook, and his computer.

After a while, Acar realized that Facebook had hidden its tracking method so that it would be more difficult to spot. Meta found a way to link the Meta Pixel tracker that’s present on around 20% of the most popular websites, including those featuring adult content, to the Facebook and Instagram apps installed on an Android phone.

Normally, the Meta Pixel tracker would send information to Meta. But Meta found a way to connect Meta Pixel to the cell phone app. This linked the web traffic it recorded to the user’s identity, as registered in Facebook and Instagram.

This allowed Meta to collect browsing information from someone’s session without asking for consent. The method also bypassed the privacy protections you might have enabled on your Android phone, like incognito mode or VPN. These are means to anonymize internet traffic and prevent anyone from tracking you. We’ve known for quite a while that incognito mode isn’t truly anonymous, but VPN protections can offer stronger privacy.

The method Meta devised ignores these protections, allowing Meta to capture all your actions on a web page and link it to your Facebook and Instagram profiles. Meta would know what products you looked at and what you bought. In turn, this will let it serve more personalized ads based on these recent activities.

Google had a stark response when asked about the new security research, providing El País with the following statement:

The developers mentioned in this report are unintentionally using functions present in many iOS and Android browsers, which blatantly violate our security and privacy principles. We have already implemented changes to mitigate these invasive techniques, launched our own investigation, and are in direct contact with the parties involved.

These remarks are especially notable considering where they’re coming from. Google recently settled a user tracking lawsuit for nearly $1.4 billion. It knows a thing or two about tracking users without consent.

Meta didn’t exactly claim responsibility. It’s referring to the incident as “an issue” that it’s working with Google to resolve. Here’s Meta’s statement on the matter:

We are speaking with Google to clarify a potential misunderstanding about how its policies are applied. As soon as we learned of the concern, we decided to pause the feature while we work with Google to resolve the issue.

Meta didn’t explain why it’s been tracking web browsing without consent. One possibility is that Google’s initiative to limit third-party tracking in browsers, which has been abandoned, motivated Meta to find other ways to track users.

Even if Meta decides not to discontinue this sort of tracking, Google is patching Chrome. Similarly, Mozilla is developing a fix to prevent such tracking. Separately, DuckDuckGo said Meta’s trackers did not affect its users.

But Meta isn’t alone in using such shady tactics. Russian company Yandex employed similar tools to track users online. Meta has only been taking this approach since September 2024, while Yandex started doing it in 2017.

Meta did protest Apple vehemently when the latter introduced strong privacy protections on the iPhone. Those features, which help users prevent tracking on apps like Facebook and Instagram, cost Meta billions in lost advertising as soon as Apple introduced them.

More recently, Meta asked Apple for unprecedented access to iPhone data under the Digital Markets Act (DMA) law in Europe. Apple has already raised alarms about Meta’s intentions:

As we strive to comply with the DMA, we carefully review each interoperability request we receive. As an example of our concerns, Meta has made 15 requests (and counting) for potentially far-reaching access to Apple’s technology stack that, if granted as sought, would reduce the protections around personal data that our users have come to expect from their devices.

If Apple were to have to grant all of these requests, Facebook, Instagram, and WhatsApp could enable Meta to read on a user’s device all of their messages and emails, see every phone call they make or receive, track every app that they use, scan all of their photos, look at their files and calendar events, log all of their passwords, and more. This is data that Apple itself has chosen not to access to provide the strongest possible protection to users.

You’ll find El Pais’ coverage at this link. Also, this website explains in great detail how Meta might have tracked your web browsing on Android.

Source

Posted on

European telcos team to gain edge, AI factories

Artificial intelligence (AI) factories are producing intelligence at unprecedented scale, showing massive potential to fuel economic growth and innovation.

To accelerate taking advantage of AI opportunities in their sector, operators Orange, Fastweb, Swisscom, Telefónica and Telenor have announced a collaboration with Nvidia to develop and expand sovereign AI factories and edge infrastructure across Europe.

The telcos believe that they are uniquely positioned to deliver AI services due to their extensive infrastructure and geographic reach. The ultimate aim of the partnership is to equip European enterprises across industries with secure, accelerated computing infrastructure to train and deploy customised AI models and agentic AI services working in a sovereign AI infrastructure.

The collaboration will see Nvidia’s full-stack technologies implemented to allow telcos to go beyond traditional connectivity services to AI as a service, driving generative and agentic AI adoption. This is also seen as empowering nations to build localised models with secure sovereign AI infrastructure.

Looking at individual companies’ deployments, the enterprise division of the Orange Group, Orange Business, has joined the Nvidia Cloud Partner programme to accelerate the development of enterprise-grade agentic AI, including its Live Intelligence platform, which is designed to enable companies to securely deploy generative AI at scale. Those AI solutions use the Orange Business Cloud Avenue platform, built on Nvidia infrastructure.

This is seen as allowing enterprises across Europe to access AI infrastructure, train custom AI models and deploy secure generative AI applications through the Orange Business’ Live Intelligence platform – as well as offer the possibility of transforming employee, customer and operational experiences.

Orange has also applied AI to its own operations, with 73,000 employees now regularly using the system to streamline tasks, develop software, automate support procedures and enhance decision-making processes. Orange’s sovereign AI infrastructure supports employees in France, as well as across Europe and Africa, and handling more than 30,000 requests daily.

Building on its creation of its host country’s first sovereign AI infrastructure, Norway’s Telenor is to expand capacity to meet rising demand from both internal teams and external customers. With plans to add an AI datacentre that will run entirely on renewable energy and contribute surplus energy back to the grid, the company believes it is helping Norway to advance its mission of secure, sovereign and sustainable AI development.

Telenor believes that since launch, its AI infrastructure has helped drive AI adoption across Norway by powering digital services for the public sector, industrial automation and local language models.

This includes hosting BabelSpeak, an AI-driven translation tool developed by Capgemini that offers near-real-time, voice-to-voice multilingual translation capabilities in nearly 100 languages and is now being piloted by Norwegian Red Cross.

Capgemini has been a key partner for Telenor to build Norway’s first sovereign and secure AI cloud service in collaboration with Nvidia.

In addition, Telenor is integrating Nvidia AI Enterprise software to accelerate enterprise adoption and deployment of generative and agentic AI applications, as well as its own internal innovation efforts, such as in network automation.

Swisscom has launched the AI Work Hub and Model catalogue, enabling enterprises across Switzerland to build complex AI projects, customise models and deploy agentic AI at scale and speed.

The operator recently announced GenAI Studio – a new service built on its Swiss AI Platform that allows enterprises to develop and run AI agents. The enterprise AI services are hosted on Swisscom’s sovereign AI factory, built on Nvidia DGX SuperPOD. This allows for scaling of capacity to serve Switzerland’s rapidly growing demand for AI services and inference, expanding the company’s revenue opportunities.

Source