Posted on

NAO: UK government cyber resilience weak in face of mounting threats

The National Audit Office (NAO) has found the UK government’s cyber resilience to be significantly behind where it needs to be, in the face of mounting and more dangerous threats.

In its Government cyber resilience report, the public spending watchdog warned that the cyber threat to the UK government is “severe and advancing quickly”. It found that 58 critical government IT systems, assessed in 2024, had significant gaps in cyber resilience, and the government does not know how vulnerable at least 228 “legacy” IT systems are to cyber attack.

The report does not cover the cyber resilience of local government, the NHS, or the nation as a whole. Fieldwork for the report was conducted between May and October 2024, with NAO staff interviewing officials from the Cabinet Office about efforts to support government departments in the implementation of the Government Cyber Security Strategy: 2022-2030.

The strategy included a target for key government organisations to be “significantly hardened to cyber attack by 2025”, but the government has not improved its cyber resilience fast enough to meet this aim, said the NAO.

The NAO also interviewed officials from the National Cyber Security Centre (NCSC) and the Central Digital and Data Office (CDDO), along with cyber security civil servants from government departments and the British Library.

The biggest risk to making the UK government resilient to cyber attack is a yawning skills gap, according to the report. It found one in three cyber security roles in government were vacant or filled by temporary – and more expensive – staff in 2023-24, while more than half of cyber roles in several departments were vacant, and 70% of specialist security architects were staff on temporary contracts.

The NAO said departments reported that salaries and civil service recruitment processes are barriers to hiring and keeping people with cyber skills.

Other concerns include a lack of coordination within government, which is jeopardising effective cyber defence. The NAO found that the respective roles of departments and central organisations, such as the NCSC, are “insufficiently understood”, and nor have departmental leaders “consistently recognised the relevance of cyber risk to their strategic goals”.

The government must act now, urged the report’s authors.

Gareth Davies, head of the NAO, said: “The risk of cyber attack is severe, and attacks on key public services are likely to happen regularly, yet government’s work to address this has been slow.

“To avoid serious incidents, build resilience and protect the value for money of its operations, government must catch up with the acute cyber threat it faces.

To avoid serious incidents, build resilience and protect the value for money of its operations, government must catch up with the acute cyber threat it faces Gareth Davies, National Audit Office

“The government will continue to find it difficult to catch up until it successfully addresses the long-standing shortage of cyber skills, strengthens accountability for cyber risk, and better manages the risks posed by legacy IT.”

Cyber resilience gaps

The NAO evaluated whether government is keeping pace with the rapidly evolving cyber threat it faces from hostile actors. It found that it is not.

It spotted that the government’s cyber assurance scheme, GovAssure, which had independently assessed 58 critical departmental IT systems by August 2024, found significant gaps in cyber resilience, with multiple fundamental system controls at low levels of maturity across departments. GovAssure assesses the critical systems of government organisations. It was set up in April 2023.

According to the NAO report, government departments were using at least 228 legacy IT systemsas of March 2024, and the government does not know how vulnerable these systems are to cyber attack.

The report noted that in April 2024, the Cabinet Office Government Security Group (GSG) reported to ministers that some departments had significantly reduced their cyber security improvement programmes to fund other priorities. This was due to “cuts to programme funding, lack of access to cyber skills, challenges with delivery partners, and delays in departmental and cross-government approvals”.

As examples of how damaging cyber attacks can be, the NAO cited the instance, in June 2024, of an attack on a supplier of pathology services to the NHS in south-east London, which led to two NHS foundation trusts postponing 10,152 acute outpatient appointments and 1,710 elective procedures. It also cited the British Library ransomware attack in October 2023, which has already cost £600,000 to rebuild its services. The library expects to spend many times more as it continues to recover.

The report also gave other examples of attacks on the Ministry of Defence and Parliament. In May 2024, the MoD’s payroll contractor’s network was compromised by an attacker – a network that held armed forces staff members’ data. Further back in time, in 2021, a Chinese state-affiliated attacker was, said the report, highly likely responsible for a cyber campaign against the parliamentary email accounts of members across both Houses of Parliament.

The report stated that in March 2024, departments did not have fully funded plans to remediate around half of government’s legacy IT assets – 53%, or 120 out of 228.

The NAO recommends the government develops, shares and starts using a cross-government implementation plan for the Government Cyber Security Strategy within the next six months. It also suggests the whole of government needs to operate differently.

Within the next year, the government should make and enact plans to fill cyber skills gaps in workforces, said the NAO.

Of the technology trumpeted most by the current and previous government – artificial intelligence (AI) – the report said: “AI can improve government’s cyber security, but it can also help threat actors looking to interfere or undermine trust in our democratic system. The NCSC is collaborating with its partners to realise the benefits of AI and protect against the associated security risks.”
Source

Posted on

Sir Alan Bates has ‘serious concerns’ over Post Office scandal compensation budget

Sir Alan Bates has “serious concerns” that the government’s budget for Post Office scandal compensation will be stretched to cover the legal costs of those making claims.

This comes as he welcomed a “very positive and quite insightful” report from the parliamentary business and trade select committee.In its report, the committee called for legally building deadlines for subpostmaster redress with financial penalties for failure.

In its Post Office and Horizon scandal redress: Unfinished business report, the committee also demanded the Post Office be removed from administering any of the redress schemes, up-front legal advice to be offered to claimants, and the appointment of independent adjudicators.

It said lawyers being paid by taxpayers should be instructed to speed up payments to subpostmasters, reduce delays, give the benefit of the doubt to claimants and publish figures on government spending on lawyers.

In February 2024, during a mammoth five-hour business and trade select committee hearing, MPs heard that the complexity and unfairness of schemes for the financial redress of former subpostmasters is leading to slow and often unfair settlements. Witnesses, including Bates, called for a legally binding deadline on when payments should be made.

A year on, and payments are still too slow. In her Autumn Budget statement in October, chancellor Rachel Reeves announced Post Office Horizon scandal compensation funding of £1.8bn.

As of November, just £499m of the £1.8bn has been paid out across four redress schemes, with 72% of the budget for redress still not paid.

Lawyers’ fees

In the report, the committee referred to oral evidence provided by Carl Creswell, director for Post Office policy and business engagement at the department of business and trade, which states that the Budget 2024 allocation of £1.8bn to settle redress costs includes claimants’ lawyers’ fees.

“I have very serious concerns about subpostmaster legal costs being taken out of the financial redress pot,” said Bates. “That money should be ring-fenced for financial redress for victims, not paying their legal costs.”

The business and trade committee said it is “imperative” that claimants are offered legal advice up-front, at no cost to themselves but paid for by the scheme administrators.  

“Years on from the biggest miscarriage of justice in British legal history, thousands of Post Office Horizon victims still don’t have the redress to which they’re entitled for the shatter and ruin of their lives … we can’t go on like this,” said chair of the committee Liam Byrne MP. “Justice delayed is justice denied.

“Victims should have up-front legal advice to help make sure they get what’s fair,” he said. “We need hard deadlines for government lawyers to approve the claims with financial penalties for taking too long. Crucially, we need the Post Office, which caused this scandal in the first place, taken out of the picture.”

Bates said the committee report shows that “at least the politicians involved can see the problems, although the civil servants in the department are blind to them”.

Recommendations welcome

Neil Hudgell at Hudgell Solicitors, which represents hundreds of former subpostmasters seeking compensation, said: “We welcome any recommendations to speed up redress, and many of these seek to remove unnecessary obstacles to justice we have seen over the past few years, repeated across hundreds of cases.

“We have repeatedly said claimants should have access to up-front legal advice in all scheme claims, that they should be given the benefit of the doubt where written evidence is limited given the timeframes we are talking, and that offers should be made at the top of the range for each category of loss. Sadly, we’ve not seen that across most schemes to this point, certainly not with any level of consistency.”

The Post Office scandal was first exposed by Computer Weekly in 2009, revealing the stories of seven subpostmasters and the problems they suffered due to the accounting software (see timeline of Computer Weekly articles about the scandal below).

Source

Posted on

Foodora tests drone and robot deliveries in Sweden

Foodora Norway, the Oslo-based subsidiary of online quick-commerce (Q-commerce) food delivery brand Foodora Group, has partnered with Nordic communications company Tele2 to pilot test home deliveries using robots and drones supported by 5G internet of things (IoT) technology.

The Stockholm metropolitan area was chosen as the test location for the ground robot and drone delivery trials. The Doora robot will be used in the ground tests while the drone trials are being conducted as part of the parallel Foodora Air project.  

A subsidiary of Berlin-based Delivery Hero, Foodora is currently present in Norway, Sweden and Finland, where the company delivers restaurant food, groceries and other consumer goods using cars and bicycles. Foodora also operates in Austria , Hungary and Czechia.

The collaboration with Tele2 forms part of Foodora’s two-year plan to roll out GPS-based robot home deliveries across the Nordic countries by in 2025 and 2026. The ambitious joint venture with Tele2 is focused on self-driving robots and drones connected to 5G and IoT technologies.

Foodora is hoping to roll out commercial Doora ground robot deliveries in Sweden and Norway by year-end 2025, with drone services introduced in 2026.  

Scandinavian countries are lagging behind the US and Finland as regards the development of self-driving robot food delivery services, said Prashant Søegaard, CEO at Foodora Norway. “Our partnership with Tele2 in Sweden will help identify the opportunities, challenges and physical obstacles we face in making Doora work as a viable and popular form of food delivery across Nordic markets,” he added.

In Finland, S-Group and its S-Market supermarket chain partnered with the Tallinn-based Starship Technologies in 2023 to roll out the Starship Robot. The first autonomous S-Market delivery robots (ADRs) became operational in selected towns during December 2023. Monitored in real-time for disruptions to service, the electric-powered Starship ADRs use artificial intelligence (AI) and GPS to plan routes and complete delivery missions.

Mobile app

The Starship Robot platform, over the five-month operating period to 30 May 2024, delivered 150,000 orders to households. Working off S-Market’s dedicated home delivery mobile app, the service had linked to an initial 100 S-Market grocery stores by the end of November.

The platform currently serves 14 towns and cities across Finland , including Helsinki , Tampere and Espoo . S-Group is estimating full-year 2024 deliveries exceeding 400,000 homes.

Additionally, S-Market is recording downloads of over 20,000 per month for the home delivery app, said Tiina Meyer, a senior business developer of retail ecommerce at S-Group.  

“The robot delivery service is a major retailing innovation boosting our grocery business,” she said. “Because of its convenience, it’s hugely popular. Customers appreciate the convenience of this new technology, the speed at which their orders are processed and delivered, the aesthetically pleasing robots, and especially enjoy the music the robots play upon delivery.”

Starship Technologies was incorporated in 2014 by Janus Friis and Ahti Heinla, the two Estonian co-founders of Skype. Headquartered in San Francisco , the company operates engineering subsidiaries in Tallinn and Helsinki .

Foodora’s pilot trials of the ground delivery Doora in Sweden include specific tests related to how the robot navigates pedestrian crossings and curbs, as well as how the robot recognises its surroundings and communicates.

Test and evaluation

The Doora and Foodora Air projects will help to test and evaluate the full potential of the delivery systems when connected to Tele2’s 5G network and IoT technology, said Stefan Trampus, the executive vice-president of Tele2 B2B.

“Within this project, we will be able to use the robot delivery concept to look at other industries and areas of use,” he said. “We can track how GPS and IoT function, and look to optimise solutions. The 5G IoT technology is essential for the drones’ smooth operation. The target is to achieve rapid response times and substantial data transfer capabilities to ensure safe delivery management.”

The Doora ground robot is designed to transport food and other products up to a maximum weight of 20kg. The delivery robot has a top speed of 6km (3.72 miles) per hour and a battery life of eight hours, with a four-hour charge.

The Foodora Air project’s core focus is on testing the operability of a fleet of battery-powered drones, utilising 5G technology provided by Tele2, to deliver meals from various restaurants located in the Stockholm suburb of Värmdö. The Nimbi drones, developed by Swedish firm Aerit, are integrated into Foodora Air’s technology platform.

The all-weather certified Nimbi drones used by Foodora Air are able to operate within a maximum delivery range of 21km and emit 2g of carbon dioxide per kilometre. The Nimbi has a maximum payload carrying capacity of 4kg (10lb), and features a proprietary winching system that enables package pick-up and drop-off without the need for supporting infrastructure.

As part of the Foodora Air trial, deliveries are being restricted to customers’ properties, including front and back gardens where packages can be safely lowered by cable from airborne drones.

The results, and shared test data, emanating from the Doora robot and Foodora Air trials in Sweden will help to shape how the company rolls out drone and robot-supported delivery services in Norway , said Søegaard. “We are closely following the tests in Sweden and hope to learn from that experience,” he said. “The data we collect from the project and trials will better inform us about the challenges we face in Norway and need to overcome and solve.”

Foodora has opened a dialogue with public and private players to expand robot delivery services across Norway . The first significant hurdle will be to obtain authorisation from the Norwegian Public Roads Administration (Statens Vegvesen), and local municipalities, ahead of launching autonomous robots, and at a later stage, drones, in Norway.

Foodora is hoping to roll out a robot delivery service in Norway during the first half of 2025, in collaboration with Danish autonomous air and ground vehicle firm Holo.

In August, Holo partnered with Foodora Norway to conduct a demonstration test at Fornebu, a suburb of Oslo , using a six-wheeled delivery robot supplied by California-based Cartken. The Cartken robot is equipped with three 5G modems and connectivity to multiple mobile operators to ensure continuous communication to shield against signal drop-off. The Cartken uses a PIN code system enabling customers to unlock and retrieve food and other deliveries.

Holo also collaborated with Posten , Norway ’s state-controlled postal service, on a pilot trial to test electric-powered delivery robot Ottobot. The robot was supplied by New York-based Ottonomy.IO. The test, which was conducted in the Oslo district of Filipstadkaia in November and December 2022, has so far not resulted in a decision by Postern to procure delivery robot units for commercial use.  

The Ottobot pilot test was run as a partnership project with AMOI, Norway ’s largest digital marketplace that connects specialist retailers, including restaurants, with customers ordering home delivery.

Posten has been something of a trailblazer in Norway as regards the testing of ground robot delivery systems. In 2018, the company conducted a pilot trial in Oslo on the Buddy Mobility autonomous parcel delivery robot. However, high operating costs and low demand for the service resulted in Posten shuttering the project in 2019.

Source

Posted on

Apple’s hallucinated AI News summaries were just disabled in iOS 18.3 beta 3

Hallucinations are a part of the early genAI experience. Since the early days of ChatGPT, we have warned that AI will make mistakes and that you should always look for sources and check whether its claims are accurate. As hard as they might have tried, the big tech players were not spared.

Google’s AI Overviews in Search delivered advice on how to put glue on pizza and hallucinate other information, forcing Google to deal with the PR mess that followed and fix the AI before releasing it to a wider audience.

Apple wasn’t spared the hallucination humiliation either, with Apple Intelligence conflating News reports to deliver fake information via the summarization feature for the News app. Apple has decided to pull the feature from the latest iOS 18 beta and deploy the needed fixes.

“With the latest beta software releases of iOS 18.3, iPadOS 18.3, and macOS Sequoia 15.3, Notification summaries for the News & Entertainment category will be temporarily unavailable,” an Apple representative told CNBC.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

Apple is working on improving the News summarization feature, which will return in a future software update. It’s unclear when the feature will be back, but Apple Intelligence continues to be a top priority for Apple’s software development teams.

As a reminder, iOS 18.4 will bring another set of AI features to iPhone, iPad, and Mac, including the smarter Siri that can control some apps and access more user data on the device to provide more helpful assistance.

Apple Intelligence’s hallucination problems went viral in December when the AI summarized several BBC reports into a single notification that started with “Luigi Mangione shoots himself.” Mangione is the alleged Brian Thompson assassin who did not shoot himself.

Other hallucinations date back to November when the AI might have shown some users The New York Times summaries that claimed Israeli Prime Minister Benjamin Netanyahu had been arrested. That wasn’t the case.

Hallucinating news is a big problem for any AI product, whether Apple Intelligence or ChatGPT. After all, we’ve been worried about AI misleading users with fake information and the manipulation risks that might come from AI products controlled by nefarious actors. Companies like Apple must get any news-related AI features right, especially summarization. Either that or not do it at all.

In addition to disabling Notification Summaries for the News and Entertainment category in iOS 18.3 beta 3, Apple has added a label to the feature noting that summaries can contain errors, as the app is in beta.

Apple made another change to how summaries appear in notifications so you can tell them apart from regular notifications. Starting with iOS 18.3 beta 3, they’ll be italicized.

Finally, Apple Intelligence users who install the latest beta can decide whether to enable or disable summaries for an iPhone app directly from the Lock Screen. Swipe to the left on a Notification Summary to get an options menu that will let you disable them for specific apps. The alternative is going into the Settings app, where you’d have customized the AI summarizations before the new beta.

As an iPhone user in the EU, I still can’t get Apple Intelligence. I couldn’t test it or experience any of the hallucination issues that US iOS 18 beta testers have encountered. Hopefully, the hallucination problem will go away by the time I get my hands on Apple Intelligence on the iPhone.

However, it’s great to see Apple admit the errors and pull the AI summarization feature entirely rather than proceeding with it without a proper fix.

Source

Posted on

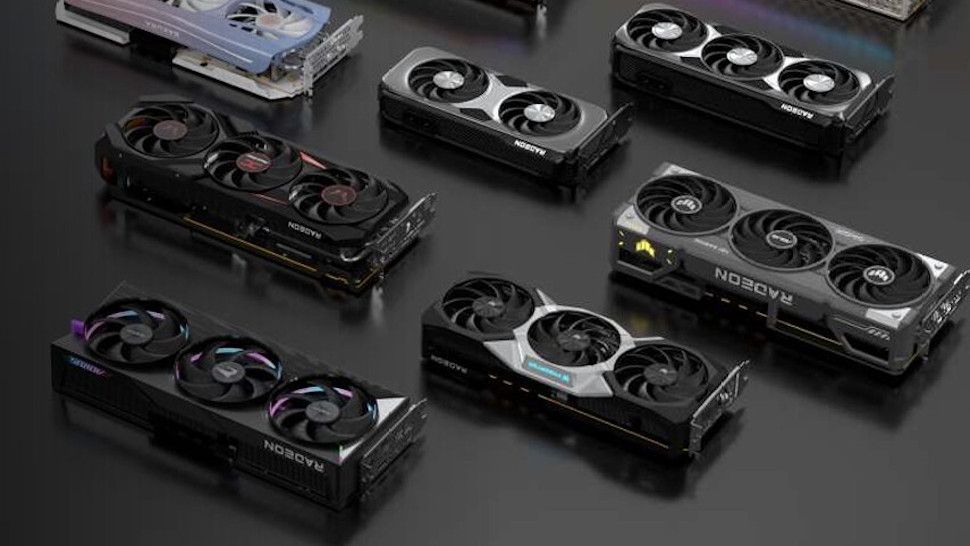
Rumor has it AMD’s feeling the heat from Nvidia’s RTX 5000 GPU launch prices – but a decision on RX 9070 pricing must be made soon

  • AMD is purportedly struggling to iron out RX 9070 pricing with retailers
  • The theory is that AMD’s original prices were too high compared to where Nvidia pitched its RTX 5000 GPUs
  • AMD needs to put all this gossip and speculation to bed as soon as possible

More rumors are circulating about AMD’s RDNA 4 graphics cards, due to launch at some point in Q1 2025, and there’s some fresh info about what could potentially be going on behind the scenes.

There’s no denying that the reveal of RX 9070 models at CES 2025 was confusingly brief, though an AMD exec has since clarified why – namely the lack of time for Team Red’s presentation at that event (a flimsy excuse, yes), and an apparent admission (possible translation issues must be noted, mind) that the company wanted to wait and see how Nvidia pitched its RTX 5000 GPUs.

Fresh speculation (via VideoCardz) from a forum moderator (Pokerclock, who recently brought us gossip on Nvidia’s Blackwell stock levels) at German site PC Games Hardware throws something else into the mix.

Namely a theory that pricing for RX 9070 models has proved problematic and that MSRPs have not been officially agreed, because the price tags AMD planned originally ended up too high compared to what Nvidia announced with its next-gen Blackwell graphics cards.

Pokerclock asserts that there are difficulties in rejigging that price and working out how to balance and correct this with what retail partners already paid for these RDNA 4 products. Working out this – and we must be extremely cautious around this rumor – is what’s apparently causing some trouble for AMD, and kind of leaving its RX 9070 graphics cards in a state of launch limbo, as it were.

An AMD Radeon RX 7900 XTX on a table against a white backdrop

(Image credit: Future)

Analysis: Time to take action, AMD

Could there be something in this? Well, it does make sense in some ways, by which I mean that Nvidia’s RTX 5070 and 5080 pricing was certainly surprising – it caught me off guard, and likely AMD, too, I’d imagine. Also, it does fit with what’s happened in terms of AMD’s sort of ‘half-launch’ at CES 2025, and the fact that we still haven’t got a date for the proper launch (an event that could be coming this week, if rumors are right – on January 23 or 24, but that’s very close at hand now, obviously).

Moreover, there are multiple sightings of the RX 9070 graphics cards having arrived at retailers, so that also suggests that the pieces of the launch were all fitting into place, and then suddenly an Nvidia-shaped spanner was chucked into the RDNA 4 works when Blackwell pricing was revealed.

{ window.reliablePageLoad.then(() => { var componentContainer = document.querySelector(“#slice-container-newsletterForm-articleInbodyContent-EWej4GxGwAxjRCyM9d3FQT”); if (componentContainer) { var data = {“layout”:”inbodyContent”,”header”:”Get daily insight, inspiration and deals in your inbox”,”tagline”:”Sign up for breaking news, reviews, opinion, top tech deals, and more.”,”formFooterText”:”By submitting your information you agree to the Terms & Conditions and Privacy Policy and are aged 16 or over.”,”successMessage”:{“body”:”Thank you for signing up. You will receive a confirmation email shortly.”},”failureMessage”:”There was a problem. Please refresh the page and try again.”,”method”:”POST”,”inputs”:[{“type”:”hidden”,”name”:”NAME”},{“type”:”email”,”name”:”MAIL”,”placeholder”:”Your Email Address”,”required”:true},{“type”:”hidden”,”name”:”NEWSLETTER_CODE”,”value”:”XTR-D”},{“type”:”hidden”,”name”:”LANG”,”value”:”EN”},{“type”:”hidden”,”name”:”SOURCE”,”value”:”60″},{“type”:”hidden”,”name”:”COUNTRY”},{“type”:”checkbox”,”name”:”CONTACT_OTHER_BRANDS”,”label”:{“text”:”Contact me with news and offers from other Future brands”}},{“type”:”checkbox”,”name”:”CONTACT_PARTNERS”,”label”:{“text”:”Receive email from us on behalf of our trusted partners or sponsors”}},{“type”:”submit”,”value”:”Sign me up”,”required”:true}],”endpoint”:”https://newsletter-subscribe.futureplc.com/v2/submission/submit”,”analytics”:[{“analyticsType”:”widgetViewed”}],”ariaLabels”:{}}; var triggerHydrate = function() { window.sliceComponents.newsletterForm.hydrate(data, componentContainer); } if (window.lazyObserveElement) { window.lazyObserveElement(componentContainer, triggerHydrate); } else { triggerHydrate(); } } }).catch(err => console.error(‘%c FTE ‘,’background: #9306F9; color: #ffffff’,’Hydration Script has failed for newsletterForm-articleInbodyContent-EWej4GxGwAxjRCyM9d3FQT Slice’, err)); }).catch(err => console.error(‘%c FTE ‘,’background: #9306F9; color: #ffffff’,’Externals script failed to load’, err)); ]]>

Sign up for breaking news, reviews, opinion, top tech deals, and more.

It’s notable that Moore’s Law is Dead also spilled some RDNA 4 details in his latest video on YouTube, and there was no rumored pricing, just a comment that he’s heard a lot of different rumors – from $450 (in the US) upwards.

Again, that paints a picture of everything still being rather up in the air at this late stage for RDNA 4, though the YouTuber gives us a rough guess of $499 (in the US) for the RX 9070 and $599 for the RX 9070 XT. That would, based on some purported internal benchmarks from AMD also shared by the leaker, make for a pair of RDNA 4 graphics cards that would be RTX 5070 and 5070 Ti killers.

Interesting and potentially exciting times indeed, but AMD can’t let these rumors on its next-gen GPU launch and pricing continue to simmer and bubble for too long – it needs to make a final decision on RDNA 4 pricing, if the company hasn’t already, of course. And then those prices need to be aired very soon (which might indeed happen, as noted, if the rumor mill is right).

You might also like

Source

Posted on

Nvidia RTX 5090 FE rumor claims high-end GPU gets loud

  • A new rumor suggests the RTX 5090 will use 600W of power
  • Comments in a Chinese forum point toward the new GPU being much louder
  • Other reports contradict this, however

Update: We’ve updated this story to give more context about the source of this latest rumor, while also highlighting other reports and evidence that suggest the RTX 5090 FE is in fact “very, very quiet”.

Nvidia‘s RTX 5090 promises to provide a step up from the previous generation’s RTX 4090, but that could come at a significant cost according to new rumors – and you might want to invest in a beefy power supply. However, this rumor is contradicted in some other early leaks and previews – so it looks like we won’t get the full picture until reviews for the new flagship GPU land.

As reported by Tomasz Gawronski on X, discussions within Chiphell (a Chinese forum page about the latest PC hardware) suggest that Nvidia’s RTX 5090 Founders Edition GPU will use 600W of power while being much louder compared to the 4090. This is based on what appears to be an upcoming review with the embargo set for January 24, with a post translated from Chinese that says “The editor cursed while testing… After all, the power consumption increased, the current increased, and the screaming also increased~”.

Considering the pricing of the RTX 5090 ($1,999 / £1,939 / AU$4,039) and the reported 30% performance increase (according to Blender benchmarks highlighted by VideoCardz), this rumor likely won’t bode well with anyone intent on upgrading to Team Green’s latest flagship GPU. The RTX 4090’s power consumption is 450W, and while this is still plenty, the rumored jump to 600W isn’t very appealing either.

The Chiphell rumor makes a big deal of the RTX 5090 being a noisy GPU and while there are plenty of legitimate reasons why people are worried about the noise produced by the RTX 5090, due to the built-in fans working hard to keep the powerful components cool, this should also be taken with a huge pinch of salt.

For a start, this is a comment on a Chinese-language website, so translating it, and the context, is difficult. There’s also no evidence provided (that we can see) about this claim.

Meanwhile, while we’re still waiting for in-depth looks at the RTX 5090’s performance – including how noisy it gets – there have been hints that the ‘loud RTX 5090’ rumors are wrong.

{ window.reliablePageLoad.then(() => { var componentContainer = document.querySelector(“#slice-container-newsletterForm-articleInbodyContent-NGVG5TdNPDSoiww56DXyJW”); if (componentContainer) { var data = {“layout”:”inbodyContent”,”header”:”Get daily insight, inspiration and deals in your inbox”,”tagline”:”Sign up for breaking news, reviews, opinion, top tech deals, and more.”,”formFooterText”:”By submitting your information you agree to the Terms & Conditions and Privacy Policy and are aged 16 or over.”,”successMessage”:{“body”:”Thank you for signing up. You will receive a confirmation email shortly.”},”failureMessage”:”There was a problem. Please refresh the page and try again.”,”method”:”POST”,”inputs”:[{“type”:”hidden”,”name”:”NAME”},{“type”:”email”,”name”:”MAIL”,”placeholder”:”Your Email Address”,”required”:true},{“type”:”hidden”,”name”:”NEWSLETTER_CODE”,”value”:”XTR-D”},{“type”:”hidden”,”name”:”LANG”,”value”:”EN”},{“type”:”hidden”,”name”:”SOURCE”,”value”:”60″},{“type”:”hidden”,”name”:”COUNTRY”},{“type”:”checkbox”,”name”:”CONTACT_OTHER_BRANDS”,”label”:{“text”:”Contact me with news and offers from other Future brands”}},{“type”:”checkbox”,”name”:”CONTACT_PARTNERS”,”label”:{“text”:”Receive email from us on behalf of our trusted partners or sponsors”}},{“type”:”submit”,”value”:”Sign me up”,”required”:true}],”endpoint”:”https://newsletter-subscribe.futureplc.com/v2/submission/submit”,”analytics”:[{“analyticsType”:”widgetViewed”}],”ariaLabels”:{}}; var triggerHydrate = function() { window.sliceComponents.newsletterForm.hydrate(data, componentContainer); } if (window.lazyObserveElement) { window.lazyObserveElement(componentContainer, triggerHydrate); } else { triggerHydrate(); } } }).catch(err => console.error(‘%c FTE ‘,’background: #9306F9; color: #ffffff’,’Hydration Script has failed for newsletterForm-articleInbodyContent-NGVG5TdNPDSoiww56DXyJW Slice’, err)); }).catch(err => console.error(‘%c FTE ‘,’background: #9306F9; color: #ffffff’,’Externals script failed to load’, err)); ]]>

Sign up for breaking news, reviews, opinion, top tech deals, and more.

For example, there’s a video from CES from the PC Centric channel (that you can view below), which includes an admittedly basic sound test (the presenter literally puts his ear next to the GPU), where the RTX 5090 is running “very, very quiet”, which is especially impressive as this is after a decent amount of time running the demanding Cyberpunk 2077 at maximum settings. PC Centric’s claim that “for the amount of power and the fact this is a two-slot card, that’s ridiculous,” flies in the face of the latest rumor, and from the video itself, it does indeed seem like the RTX 5090 FE will be impressively quiet – though of course we’ll again have to wait for full reviews, including our own, to really find out just how loud (or not) this monster GPU is.

Gaming On The RTX 5090 With DLSS 4! – YouTube Gaming On The RTX 5090 With DLSS 4! - YouTube Watch On

The mere fact that the RTX 5090 FE has been slimmed down to a dual-slot size, rather than the huge size of the 4090, which was a 3.5 slot behemoth, suggests that Nvidia is in fact pretty bullish about the power requirements and noise of the Founders Edition card.

As mentioned earlier, components, especially powerful GPUs, can run very hot when in use, and this often means the fans kick in to help cool it down – which can end up being distractingly noisy. To combat this, companies will often make their products larger so airflow is better. By making the RTX 5090 FE smaller than the 4090, it feels like Nvidia is confident in the efficiency and quality of the new ‘cooling innovations’ that it’s showcased ahead of launch.

According to Nvidia, the RTX 5090 Founders Edition has been designed with cooling capacity in mind, including improved Liquid Metal thermal interface material (TIM), and a unique three-piece PCB that is designed to maximise cooling without resorting to turning the fans up to max.

So, while some parts of the internet are getting concerned about the rumor from Chiphell, it seems there’s plenty of counter evidence out there that should allay some of those fears.

What does this mean in terms of PSU requirements?

When it comes to the power consumption of the new GPU, it’s again important to note that this is just a rumor, but if it’s legitimate, then RTX 5090 users will certainly have to shell out more than $1,999 / £1,939 / AU$4,039. If you don’t already own a 1000W PSU, then you’ll more than likely need to invest in one – the recommended PSU requirement for the RTX 5090 is 1000W according to Corsair.

This is especially the case if you’ve got a high-end CPU equipped, as you’ll want to avoid any system malfunctions due to your PSU not wielding enough power. Once reviews arrive, we’ll have to measure just how much of a jump the RTX 5000 series flagship GPU is from the previous generation.

If I’m honest, even the RTX 4090 is still overkill for gamers, which will also be true of the RTX 5090 – so if you invest in a new GPU and new PSU, you might have to wait a while to really get the most out of your rig.

You may also like…

Source

Posted on

Rumors are swirling that OpenAI is on the brink of AGI and ASI

We’ve been waiting for a big ChatGPT upgrade for months now, but OpenAI has yet to announce one. Sure, the company had a monster month of announcements in December. OpenAI took the o1 reasoning model out of beta, making it available to more ChatGPT users. The text-to-video Sora tool is now available to users in certain markets. The o3 reasoning model has also been announced and is currently undergoing testing.

These are just a few of the AI announcements OpenAI made in December, but there’s no word on when the GPT-4o upgrade will drop. Unofficially, reports say that ChatGPT GPT-5, or whatever it ends up being called, is running behind schedule, as OpenAI has had issues training the next-gen AI model. OpenAI isn’t the only AI company experiencing such problems.

Sam Altman has been hyping OpenAI’s accomplishments recently, teasing potential ChatGPT features to come in 2025 while also talking about the larger goals. AGI (artificial general intelligence) is the next big thing, an AI that can tackle any task just like a human would. After AGI, we get to artificial superintelligence (ASI), which is AI that exceeds the capabilities of the human mind.

“We are now confident we know how to build AGI as we have traditionally understood it,” Altman said in a blog post recently, adding that OpenAI is already starting to look at superintelligence development.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

How close are we to that big AI breakthrough? Some people think the recent excitement that some OpenAI engineers are displaying online suggests that the company is indeed close to some sort of big advancement in AI.

Some AI fans noticed the recent teasers from OpenAI employees, as well as an essay from an AI researcher who goes by the name of “Gwern” online.

Gwern theorized that OpenAI may hold the key to developing AGI and superintelligence. A powerful reasoning model like the o1 or o1 pro can produce the data needed to train more advanced reasoning models.

The essay author in the tweet above also said they’re surprised OpenAI isn’t keeping o1-pro private so they can use it for training o3 and newer models. Eventually, AI models will train themselves, leading to the big AGI and ASI breakthroughs we’re waiting for.

Gwern suggests that OpenAI may already be on the verge of a big breakthrough, or they’ve already done it behind closed doors:

If you’re wondering why OAers are suddenly weirdly, almost euphorically, optimistic on Twitter, watching the improvement from the original 4o model to o3 (and wherever it is now!) may be why. It’s like watching the AlphaGo Elo curves: it just keeps going up… and up… and up… 

There may be a sense that they’ve ‘broken out’ and have finally crossed the last threshold of criticality, from merely cutting-edge Al work, which everyone else will replicate in a few years, to takeoff – cracked intelligence to the point of being recursively self-improving and where o4 or o5 will be able to automate AI R&D and finish off the rest.

This isn’t just about OpenAI being close to the next massive improvement in AI but also the future beyond that. Access to superintelligence will make subsequent AI developments easier and more efficient because an AI mind will handle the next innovations.

Also, in a scenario where OpenAI might be close to AGI and ASI, it would obtain an incredible advantage over competitors. Other AI firms that have not established their own superintelligence will have to develop AI with traditional methods. In contrast, OpenAI would have ASI employing its own discoveries to create better AI, and it’ll do it more efficiently.

This is all speculation at this point, as OpenAI has yet to make any announcements. But it’s all based on the recent hype from Sam Altman and other OpenAI engineers. Of course, they always seem to go out of their way to hype OpenAI’s efforts on social media, so this all could simply be more of the same.

Also, if and when ChatGPT AGI and ASI are reached, don’t expect it to be affordable or even available publicly. At least, not initially. OpenAI rivals might be just as close to AGI and ASI, but they might be more restrained in teasing imminent breakthroughs.

Finally, there’s also the safety aspect to consider. Artificial intelligence, from the current ChatGPT models to AGI and ASI, will have to be aligned with humanity’s interests so it doesn’t develop its own agenda, which could almost certainly endanger our species.

Back to GPT-5, it’ll still be interesting to see what OpenAI does next in terms of ChatGPT upgrades. More news about o3 should come soon. Then, GPT-4o will celebrate its first anniversary this summer. Some sort of upgrade for the base ChatGPT model is surely due soon.

Source

Posted on

Corporate cover-up behind world-beating cyber security record in Middle East

Only two of the top 100 listed companies in the Middle East reported cyber security incidents last year, according to defence vulnerability scanning firm SecurityScorecard, but most incidents in the region went unreported, it said. 

SecurityScorecard’s findings highlighted an impressive record in the Middle East and North Africa (MENA) when compared with Europe, where 18 of the top 100 firms had security breaches, and to the US, where 21% of firms in the S&P 500 stock market index were hit. 

Gulf states in particular have invested heavily in cyber security to deter rampant attacks in the region as they transform from central, state-controlled petro-states to diverse economies more dependent on vulnerable information communications. But experts said it still lagged EU and US in laws required to guarantee open reporting deemed necessary for resilience. 

Ryan Sherstobitoff, vice-president of research at SecurityScorecard, said he believed most security breaches that large MENA corporations suffered last year went unreported. 

“I would say probably 80% is not reported,” he said. “The Middle East isn’t exactly required to report breaches in the same way as North America, or even some locations in Europe. So, it’s never going to be recorded.”

When a MENA security breach did become public, it was usually because hackers had hit the subsidiary of a foreign corporation whose home rules required it to report the incident, said Sherstobitoff. Moreover, the geopolitical situation spawned more attacks than elsewhere. Four-fifths of the top 100 MENA corporations are in Gulf countries – usually state-owned banks, energy firms and utilities. 

The would-be ratings agency noted a correlation between firms that reported no breaches and those it scored ‘A’, after assessing detailed scans it did of their security vulnerabilities, along with incident reports. Breaches diminish a firm’s rating significantly, but only briefly, according to its methodology. 

It gave half the top 100 MENA firms A ratings – twice as many as Europe, and a fifth more than the US S&P 500. SecurityScorecard rated 84 of the 100 as either A or B. The strength of MENA cyber security, widely attributed to massive investment, was confirmed in the ITU global index, with Gulf economies ranked among the most secure in the world. 

MENA incident reports that appear more reliable involve indirect attacks, with 84 of the top 100 firms admitting they suffered breaches caused by the mistakes of their suppliers, according to SecurityScorecard. Almost every single top EU firm reported the same. A spokesperson said that it has not produced comparable third party breaches of US firms. 

Ross Brewer, an expert with deep experience of high-level security in the region, said MENA’s immense spending on cyber resilience was not as good in reality as on paper. “In Western societies, bad news travels fast. In the Middle East, if the government has anything to do with it, bad news does not travel at all. When you are building a utopian future that will attract global tourists, you want to present the absolute best image,” he said. 

Firms “in these pretentious countries” did not report incidents because the culture encouraged dignified face-saving, said Brewer. Intense government control of all communications in and out of the region, and internally, was effective at catching attackers. But MENA investment in cyber defences, according to Brewer, had been hasty, shoddy and done piecemeal by expats who left behind them a fractured and vulnerable security architecture. People were afraid to speak out, he claimed. 

Bharat Raigangari, board adviser to Dubai security consultancy 1CxO, a company which large firms in the region, said an independent security ratings agency was just what the region needed to address the security problems implied by its third party breaches. Raigangari said was trying to create one, with the backing of the UAE cyber security Council, “but it is much easier said than done”.

It was true MENA had fewer reported incidents because firms were not inclined to report them, he said. But the region’s security, and its regulations, were maturing fast and catching up with the West. 

Experts in the region applaud state authorities for their progress in building cyber defences and enacting legislation. 

Yedhu Krishna Menon, head of third-party cyber security at a MENA bank, who asked for his employer to remain anonymous because it is culturally unacceptable to reveal it, said that reported incidents were low because the region’s defences were particularly good. 

Whereas hiding security breaches to save face was not limited to MENA, a bigger concern is “reputation damage, fear of negative publicity, of stigma – it’s a global thing”, he said. 

“They don’t report the majority because they don’t want to lose business,” he added. MENA culture had also progressed. “It’s not like 10 years back.” 

Attackers, aiming to bring down economies and exploit vulnerabilities introduced by the region’s transforming economies, had merely prompted MENA countries to implement regulation to drive investment in security. The regulatory impetus had been momentous and like nowhere else in the world, said Menon. 

Munir Subor, a partner at law firm Taylor Wessing in Dubai, said that it was common practice for firms in the region not to report incidents. Those reported to government would remain secret. 

Nick Loumakis, MENA managing director at Obrela, a Greek firm working closely with UAE cyber security authorities, believed the region’s low incident numbers were correct. 

Government was “always in the room” whenever he had dealt with an incident, but he knew of only one large firm hit in the past two years. He didn’t think saving face played a factor. “It’s not easy to keep this information hidden,” he said, believing that government control of large firms and an oligarchical economy has allowed MENA countries to stamp out attackers more effectively. 

MENA state authorities contacted by Computer Weekly were unavailable for comment. 

Source

Posted on

US Treasury incident a clear warning on supply chain security in 2025

A major state-sponsored cyber incident that targeted the United States Department of the Treasury in the weeks prior to Christmas 2024 appears to have begun as the result of a compromise at a third-party tech support supplier, serving as a warning on the precarious security and vulnerable nature of technology supply chains for IT firms and their customers alike.

The cyber attack was allegedly the work of an undisclosed China-backed advanced persistent threat (APT) actor and, according to The Washington Post, it targeted among other things the Office of Foreign Assets Control (OFAC), a department of the Treasury that administers and enforces foreign sanctions against individuals, organisations and countries.

Due to its involvement in sanctions and enforcement actions against malicious cyber actors – it has played a key role in multinational operations against financially motivated ransomware gangs – OFAC presents a very obvious target for threat actors.

In a letter to senators Sherrod Brown and Tim Scott, who sit on the Committee on Banking, Housing and Urban Affairs – a copy of which has been reviewed by Computer Weekly – Treasury assistant secretary for management, Aditi Hardikar, confirmed the department was notified by a third-party software services provider that it had been compromised on 8 December 2024.

The organisation in question, BeyondTrust, said the APT gained access to a key that it was using to secure a cloud-based remote tech support service.

“With access to the stolen key, the threat actor was able override the service’s security, remotely access certain Treasury DO user workstations, and access certain unclassified documents maintained by those users,” wrote Hardikar.

“Treasury has been working with the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), the Intelligence Community, and third-party forensic investigators to fully characterise the incident and determine its overall impact.

“Based on available indicators, the incident has been attributed to a China state-sponsored APT  actor. The compromised BeyondTrust service has been taken offline and at this time there is no evidence indicating the threat actor has continued access to Treasury information,” wrote Hardikar.

The Chinese authorities have denied the Americans’ allegations, with a spokesperson for Beijing’s embassy in Washington DC describing them as “irrational” and part of a “smear campaign”.

BeyondTrust vulnerabilities

The tech firm at the centre of the incident, BeyondTrust, is a US-based supplier with roots dating back to the mid-1980s. It specialises in privileged identity management and privileged access management (PIM/PAM), privileged remoter access and vulnerability management services. It claims more than 20,000 customers in 100 countries, including the likes of tech firms such as Axians and ServiceNow.

It is also particularly well-used in the public sector, with multiple customers in local government, healthcare and utilities, including a number of NHS bodies in the UK.

In a statement posted to its website, BeyondTrust said it identified an incident impacting a “limited number” of Remote Support SaaS customers that arose through the compromise of an application programming interface (API) key. It revoked the key immediately on concluding a root cause analysis into a remote support SaaS technical issue on 5 December 2024, and began notifying affected users, including the Treasury.

It has since identified two specific vulnerabilities within the Remote Support and Privileged Remote Access product lines – one of critical severity and one of medium severity. These have been assigned designations CVE-2024-12356 and CVE-2024-12686 respectively. Both have been patched for both cloud-hosted and on-prem versions as of 18 December 2024.

According to BeyondTrust, the issues are both command injection vulnerabilities that, successfully exploited, enable an unauthenticated remote attacker to execute operating system commands in the context of the site user.

A BeyondTrust spokesperson told Computer Weekly: “BeyondTrust previously identified and took measures to address a security incident in early December 2024 that involved the Remote Support product. BeyondTrust notified the limited number of customers who were involved, and it has been working to support those customers since then. No other BeyondTrust products were involved. Law enforcement was notified and BeyondTrust has been supporting the investigative efforts.”

Security supply chain still a big issue in 2025

With this incident, BeyondTrust unfortunately becomes the latest in a long-line of cyber security specialists to find themselves making headlines after the compromise of products and solutions designed to keep end-users safe.

Avishai Avivi, CISO at SafeBreach, a supplier of breach and attack simulation tools, explained how the breach likely unfolded. “BeyondTrust, unironically, provides a secure method for IT support personnel to provide remote support to end users,” he said. “This method involves establishing a trusted connection between the support person and the end-user.

“This trusted connection punches through traditional perimeter security controls and gives the support person full access and control over the end-user workstation. Once inside, the support person can send documents back over that secure channel or masquerade as the end-user and send the same documents directly.

“The security controls protecting the US Treasury network have no way of knowing something nefarious is happening, as the trusted connection is, well, trusted.

“Was there something that the US Treasury could have done to prevent this? The sad answer appears to be yes. Again, referring to the technical information BeyondTrust provided, the system administrators at the US Treasury, or the vendor likely to provide support services, failed to configure trusted locations from which the support agents could connect. We refer to this as IP whitelisting [allowlisting].

“This failure is a critical risk with any such service [and] the same issue led to notable breaches in 2023 and 2024. This oversight is why we urge all service vendors, especially trusted ICT vendors, to follow the CISA Secure-by-Default guidance.”

Source

Posted on

TikTok ban still on track as Supreme Court rejects appeal

On Friday, the Supreme Court rejected an appeal from TikTok and parent company ByteDance, allowing the ban set to take place this weekend to go forward.

The Supreme Court was effectively TikTok’s last chance to sidestep divestiture or a nationwide ban in the United States. The court didn’t find TikTok’s argument that banning its popular video-sharing app would be a violation of the First Amendment compelling.

The Supreme Court did acknowledge that “TikTok offers a distinctive and expansive outlet for expression, means of engagement, and source of community” for 170 million Americans. “But Congress has determined that divestiture is necessary to address its well-supported national security concerns regarding TikTok’s data collection practices and relationship with a foreign adversary,” the justices concluded.

Therefore, the Protecting Americans from Foreign Adversary Controlled Applications Act will go into effect on January 19, which means TikTok and ByteDance have hours to decide whether to cease operations in the US or find a buyer.

Tech. Entertainment. Science. Your inbox.

Sign up for the most interesting tech & entertainment news out there.

By signing up, I agree to the Terms of Use and have reviewed the Privacy Notice.

According to CNN, the Biden administration will leave it up to President-elect Donald Trump to enforce the ban, which Trump now says he wants to reverse.

“Our position on this has been clear,” a Biden official said. “TikTok should continue to operate under American ownership. Given the timing of when [the Protecting Americans from Foreign Adversary Controlled Applications Act] goes into effect over a holiday weekend a day before inauguration, it will be up to the next administration to implement.”

Barring a surprise extension by President Biden, there’s a good chance that TikTok will no longer be accessible in the United States (at least temporarily) as of Sunday.

Source